> ## Documentation Index
> Fetch the complete documentation index at: https://docs.oleria.ai/llms.txt
> Use this file to discover all available pages before exploring further.
# AI Agent Gateway
> Let AI agents work in your SaaS applications without ever holding a credential - with your own permissions, your company's policy, and a full audit trail applied to every call.
AI agents are useful only when they can reach the applications your work lives in. Getting them there usually means handing over a token - pasting a personal access token into a chat window, signing a CLI in on the agent's behalf, or baking a service-account key into a config file. That credential is long-lived, reusable, and sits outside your control. Nothing checks the agent's next action before it runs, and the audit trail shows a token, not a person.
The Oleria AI Agent Gateway removes the credential from the agent entirely. The agent calls the gateway, the gateway injects the credential, applies your permissions and your company's policy, and records what happened. The agent never sees a secret.
## How the gateway works
1. **An administrator enables applications** - an Oleria Administrator chooses which applications agents are allowed to reach. Nothing is reachable through the gateway until it's enabled.
2. **An administrator sets the policy** - for each enabled application, they decide what happens when an agent attempts a high-impact action: allow it, alert on it, hold it for approval, or deny it outright.
3. **You connect your applications** - you authorize each application once, from the Governance App. Oleria holds the resulting credential; your agent never receives it.
4. **You connect your AI agent** - you add the gateway to your agent as an MCP connector and sign in once.
5. **Your agent works on your behalf** - every call the agent makes runs through the gateway, tied to your identity, with Oleria injecting the credential for the target application.
6. **Policy is applied to every call** - the gateway allows, alerts, holds for approval, or denies each action before it reaches the application.
7. **Everything is recorded** - every call is logged with the agent, session, application, and action, tying each entry back to a person rather than to a shared token.
For OAuth applications, the gateway can't give an agent more access than you already have. The credential is the one you authorized, so your permissions in the target application still apply, and policy can only narrow them further.
Non-OAuth applications work differently. They use a credential supplied by an administrator or application owner rather than one tied to you, so the access it carries is whatever that credential holds. Policy and the audit trail still apply to every call.
## What you can connect
| Access type | What it covers | How access is granted |
| :--------------- | :---------------------------------------------------------------------------------------------------------------------- | :---------------------------------------------------------------------------------- |
| OAuth access | Applications that support OAuth, such as GitHub, Google Workspace, Jira, Confluence, Salesforce, SharePoint, and Slack. | You authorize the application once, and Oleria stores and injects the token. |
| Non-OAuth access | Applications reached with an API key or token rather than an OAuth flow. | An administrator or owner supplies the credential, which Oleria stores and injects. |
## The two consoles
The gateway has an administrator surface and an end user surface. They show the same applications from different sides.
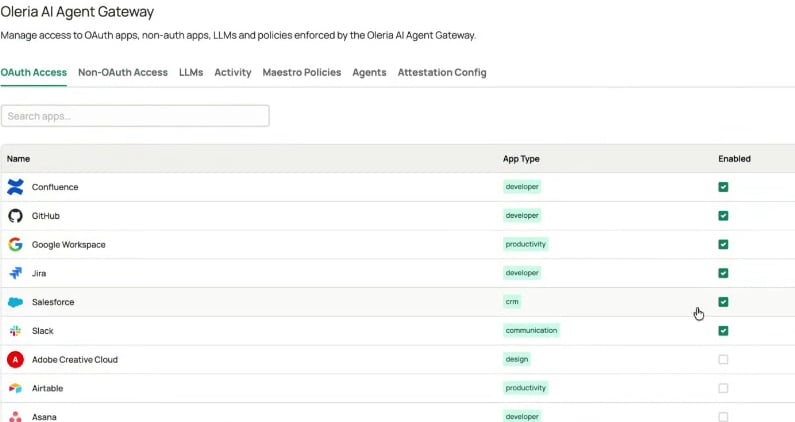
**Administrators** work in the Oleria admin portal at `youroleriainstancename.oleria.io`, under **Governance** -> **Oleria AI Agent Gateway**. This is where applications are enabled and policy is set, for everyone. See [Administrator setup](/governance/ai-agent-gateway-admin-setup).
 **Everyone else** works in the Governance App at `youroleriainstancename-governance.oleria.io`, under **AI Agent Gateway**. This is where you connect your own applications and see your own activity. See [User setup](/governance/ai-agent-gateway-user-setup) and [Connect and use your AI agent](/governance/ai-agent-gateway-connect-agents).
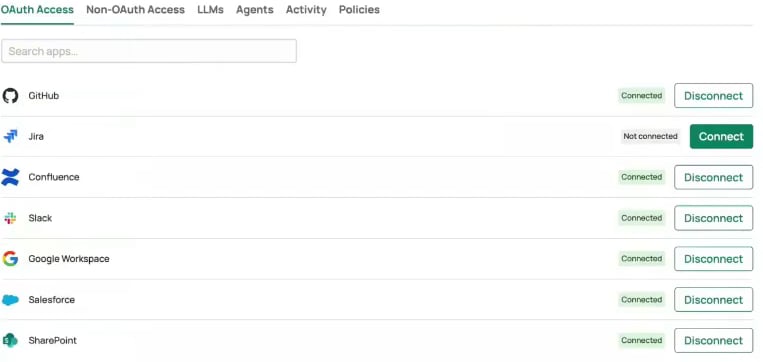 The same application appears on both sides. An administrator decides whether it can be used at all and what an agent may do in it; you decide whether to connect your own account to it.
## Contact us
For questions, contact us at [support@oleria.com](mailto:support@oleria.com).