This page is about signing in to Oleria and provisioning Oleria accounts from Entra ID. It is not the same as the Microsoft Entra ID integration under Integrations, which connects Entra as a read-only data source so Oleria can analyze your Entra tenant’s identities and access - that integration doesn’t affect who can sign in to Oleria or how.
Overview
Main Workspace vs. Governance App
Oleria has two independent surfaces, each with its own sign-in and provisioning configuration:- Main Workspace - where administrators, operators, and analysts run Oleria itself: posture, access graph, workflows, and settings.
- Governance App - a separate portal where reviewers and approvers complete access reviews, act on access requests, and work governance queues. Governance app users are a distinct population from workspace users, typically much larger (anyone in the org who might approve or review something), and usually don’t need any other access to Oleria.
SSO vs. SCIM vs. automatic user provisioning
Oleria has three related but independent mechanisms. SSO is for authentication only, where as SCIM and automatic user provisioning are for provisioning.
See Automatically provision reviewers for the full detail on that setting - Part 2 of this page is about SCIM, not automatic user provisioning.
Possible provisioning flows
Because these mechanisms are independent, and each applies per workspace (Main Workspace vs Governance App), several combinations are all valid. Pick the one that matches what you’re trying to achieve before you start:
This page sets up the recommended SSO + SCIM flow. If you’d rather use automatic user provisioning instead of SCIM for the Governance App, see the note at the end of Part 2. If you need both Oleria workspaces connected to Entra, read the next section before creating a second enterprise application.
Entra’s one-app-per-Entity-ID rule
Microsoft Entra requires every SAML relying party - every enterprise application configured for SAML SSO - to have a unique Entity ID (Identifier) within the tenant:“There cannot be two applications in a single Microsoft Entra tenant with the same entity identifier.” - Microsoft LearnEntra enforces this because it uses the Entity ID to work out which application should receive a given SAML response; without a unique identifier per app, it can’t disambiguate. This is sometimes described as one Entity ID per “relying party trust” (RPT) - that’s not a separate object you configure, it’s just what Entra calls an application once it’s set up for SAML SSO. Every enterprise app with SAML SSO configured is a relying party trust; there’s no way to do SAML SSO without one, and no way around the uniqueness rule by avoiding the term. This collides with Oleria’s design: as the SSO configuration page notes, the Main Workspace and Governance App tabs show the same Entity ID and ACS URL, because they share one Oleria service provider. If you create two separate Entra enterprise apps - one per Oleria workspace - both need Oleria’s Entity ID, and Entra will reject the second one with an error like “please enter an identifier which is unique within your organization.” The fix: use a single Entra enterprise application for both workspaces, rather than creating two. Complete Part 1 once to create that one app, then when you reach the SSO Configuration Governance App tab in Oleria, add its identity provider using the same Entra app’s federation metadata URL instead of creating a second app. One Entra app, one Entity ID, satisfies Entra’s rule, and both Oleria workspaces get a working IdP.
A single shared Entra app means the same set of assigned Entra users/groups can sign in through either workspace - Entra assignment doesn’t distinguish which Oleria workspace a sign-in is destined for, since that’s determined by which button the user selects on Oleria’s own sign-in page. If you need a genuinely different population gated at the identity provider for each workspace, don’t reuse one Entra app; instead, connect Entra to only one workspace and use a different IdP, or manual provisioning, for the other.
Prerequisites
- Administrator access to your Oleria workspace, and Global Administrator (or equivalent) access in Entra to create and configure enterprise applications.
- Decide which workspace(s) - Main Workspace, Governance App, or both - you’re connecting Entra to, and whether you want SSO, SCIM, or both for each. See Possible provisioning flows above.
- For SCIM into the Main Workspace: know which Oleria roles (
admin,operator,analyst,governance-operator,identity-lifecycle-operator) your Entra groups should map to. See How Oleria maps roles and groups. - For SCIM: a Microsoft Entra ID P1 or P2 license. Automatic provisioning is a premium Entra feature, and provisioning groups - which is how the Main Workspace grants roles - requires P1 at minimum. Check this before you start. See Entra ID P1 or P2 is required for SCIM below. SSO (Part 1) works on Entra ID Free, except for token encryption, which also needs P1 or P2.
Part 1: Set up SSO
1
Open Oleria's SSO configuration page
In Oleria, go to Settings → SSO Configuration, select the Main Workspace or Governance App tab depending on which one you’re connecting first, and click Add IdP in the SAML IdP card.
2
Create the Entra enterprise application
In the Microsoft Entra admin center, go to Entra ID → Enterprise applications → New application → Create your own application, select Non-gallery application, and name it something that identifies it as the Oleria connection (for example
Oleria) - if you plan to share this one app across both workspace, avoid naming it after just one workspace.3
Copy Oleria's SP details into Entra
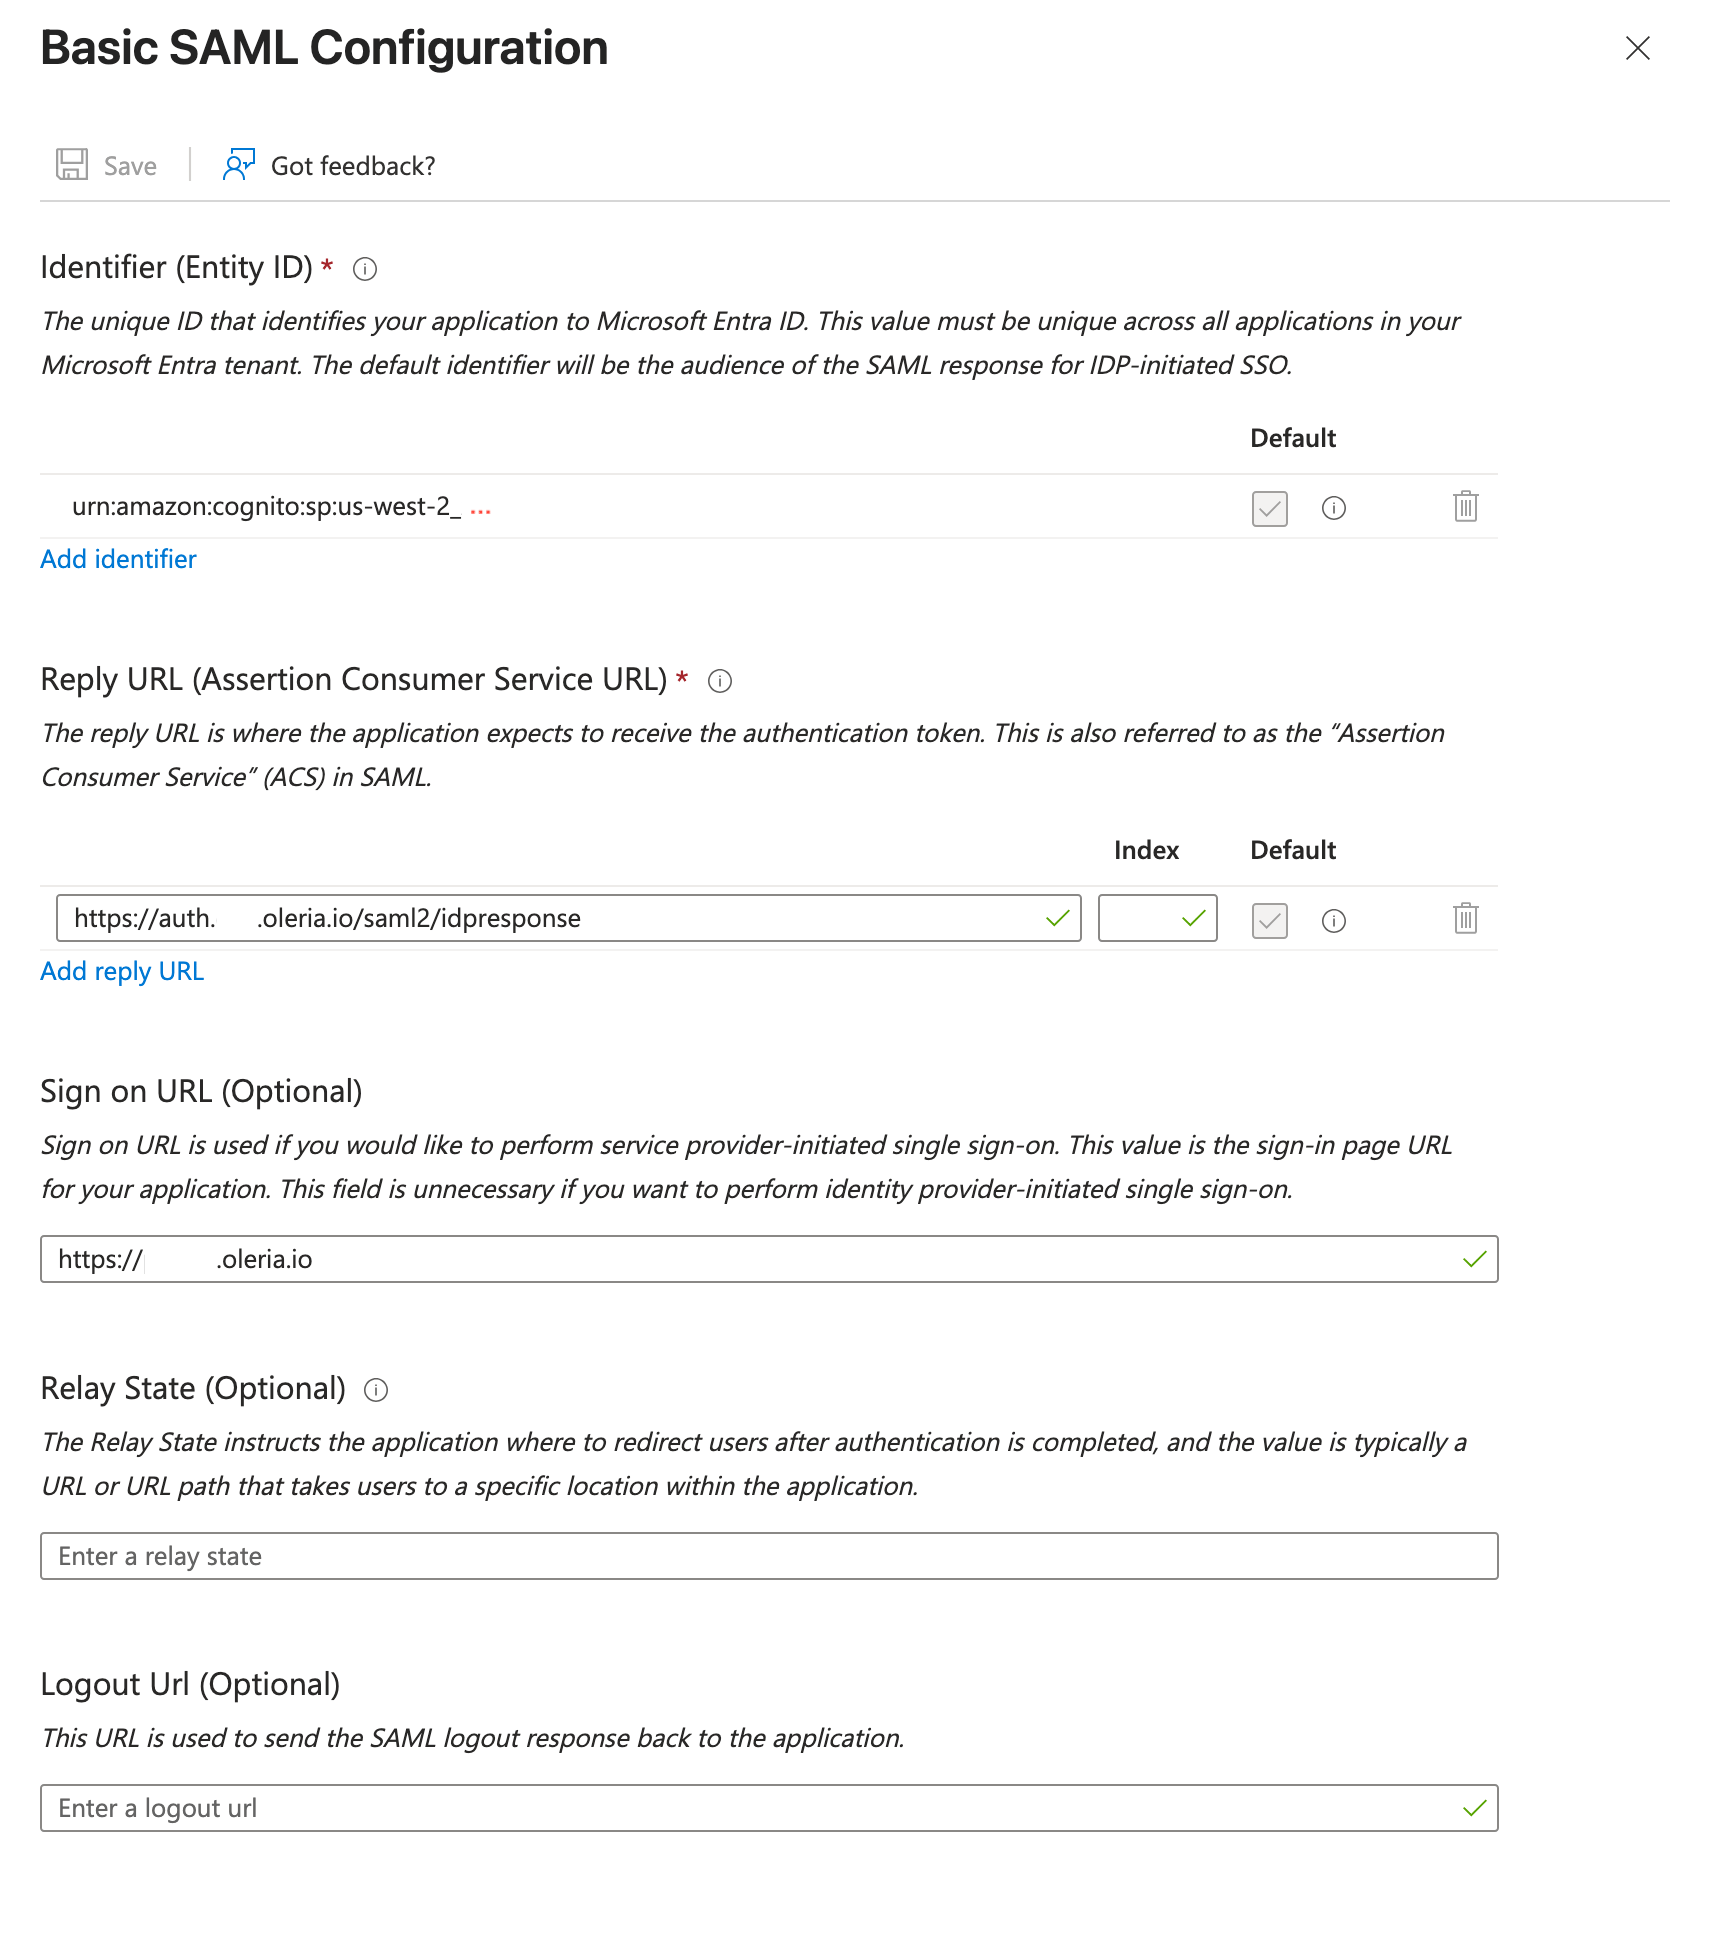
On Oleria’s Oleria details step, copy the Entity ID and ACS URL. In the Entra app, select Single sign-on → SAML → Basic SAML Configuration, and enter them as the Identifier and Reply URL. Click Save and close the panel.Navigation: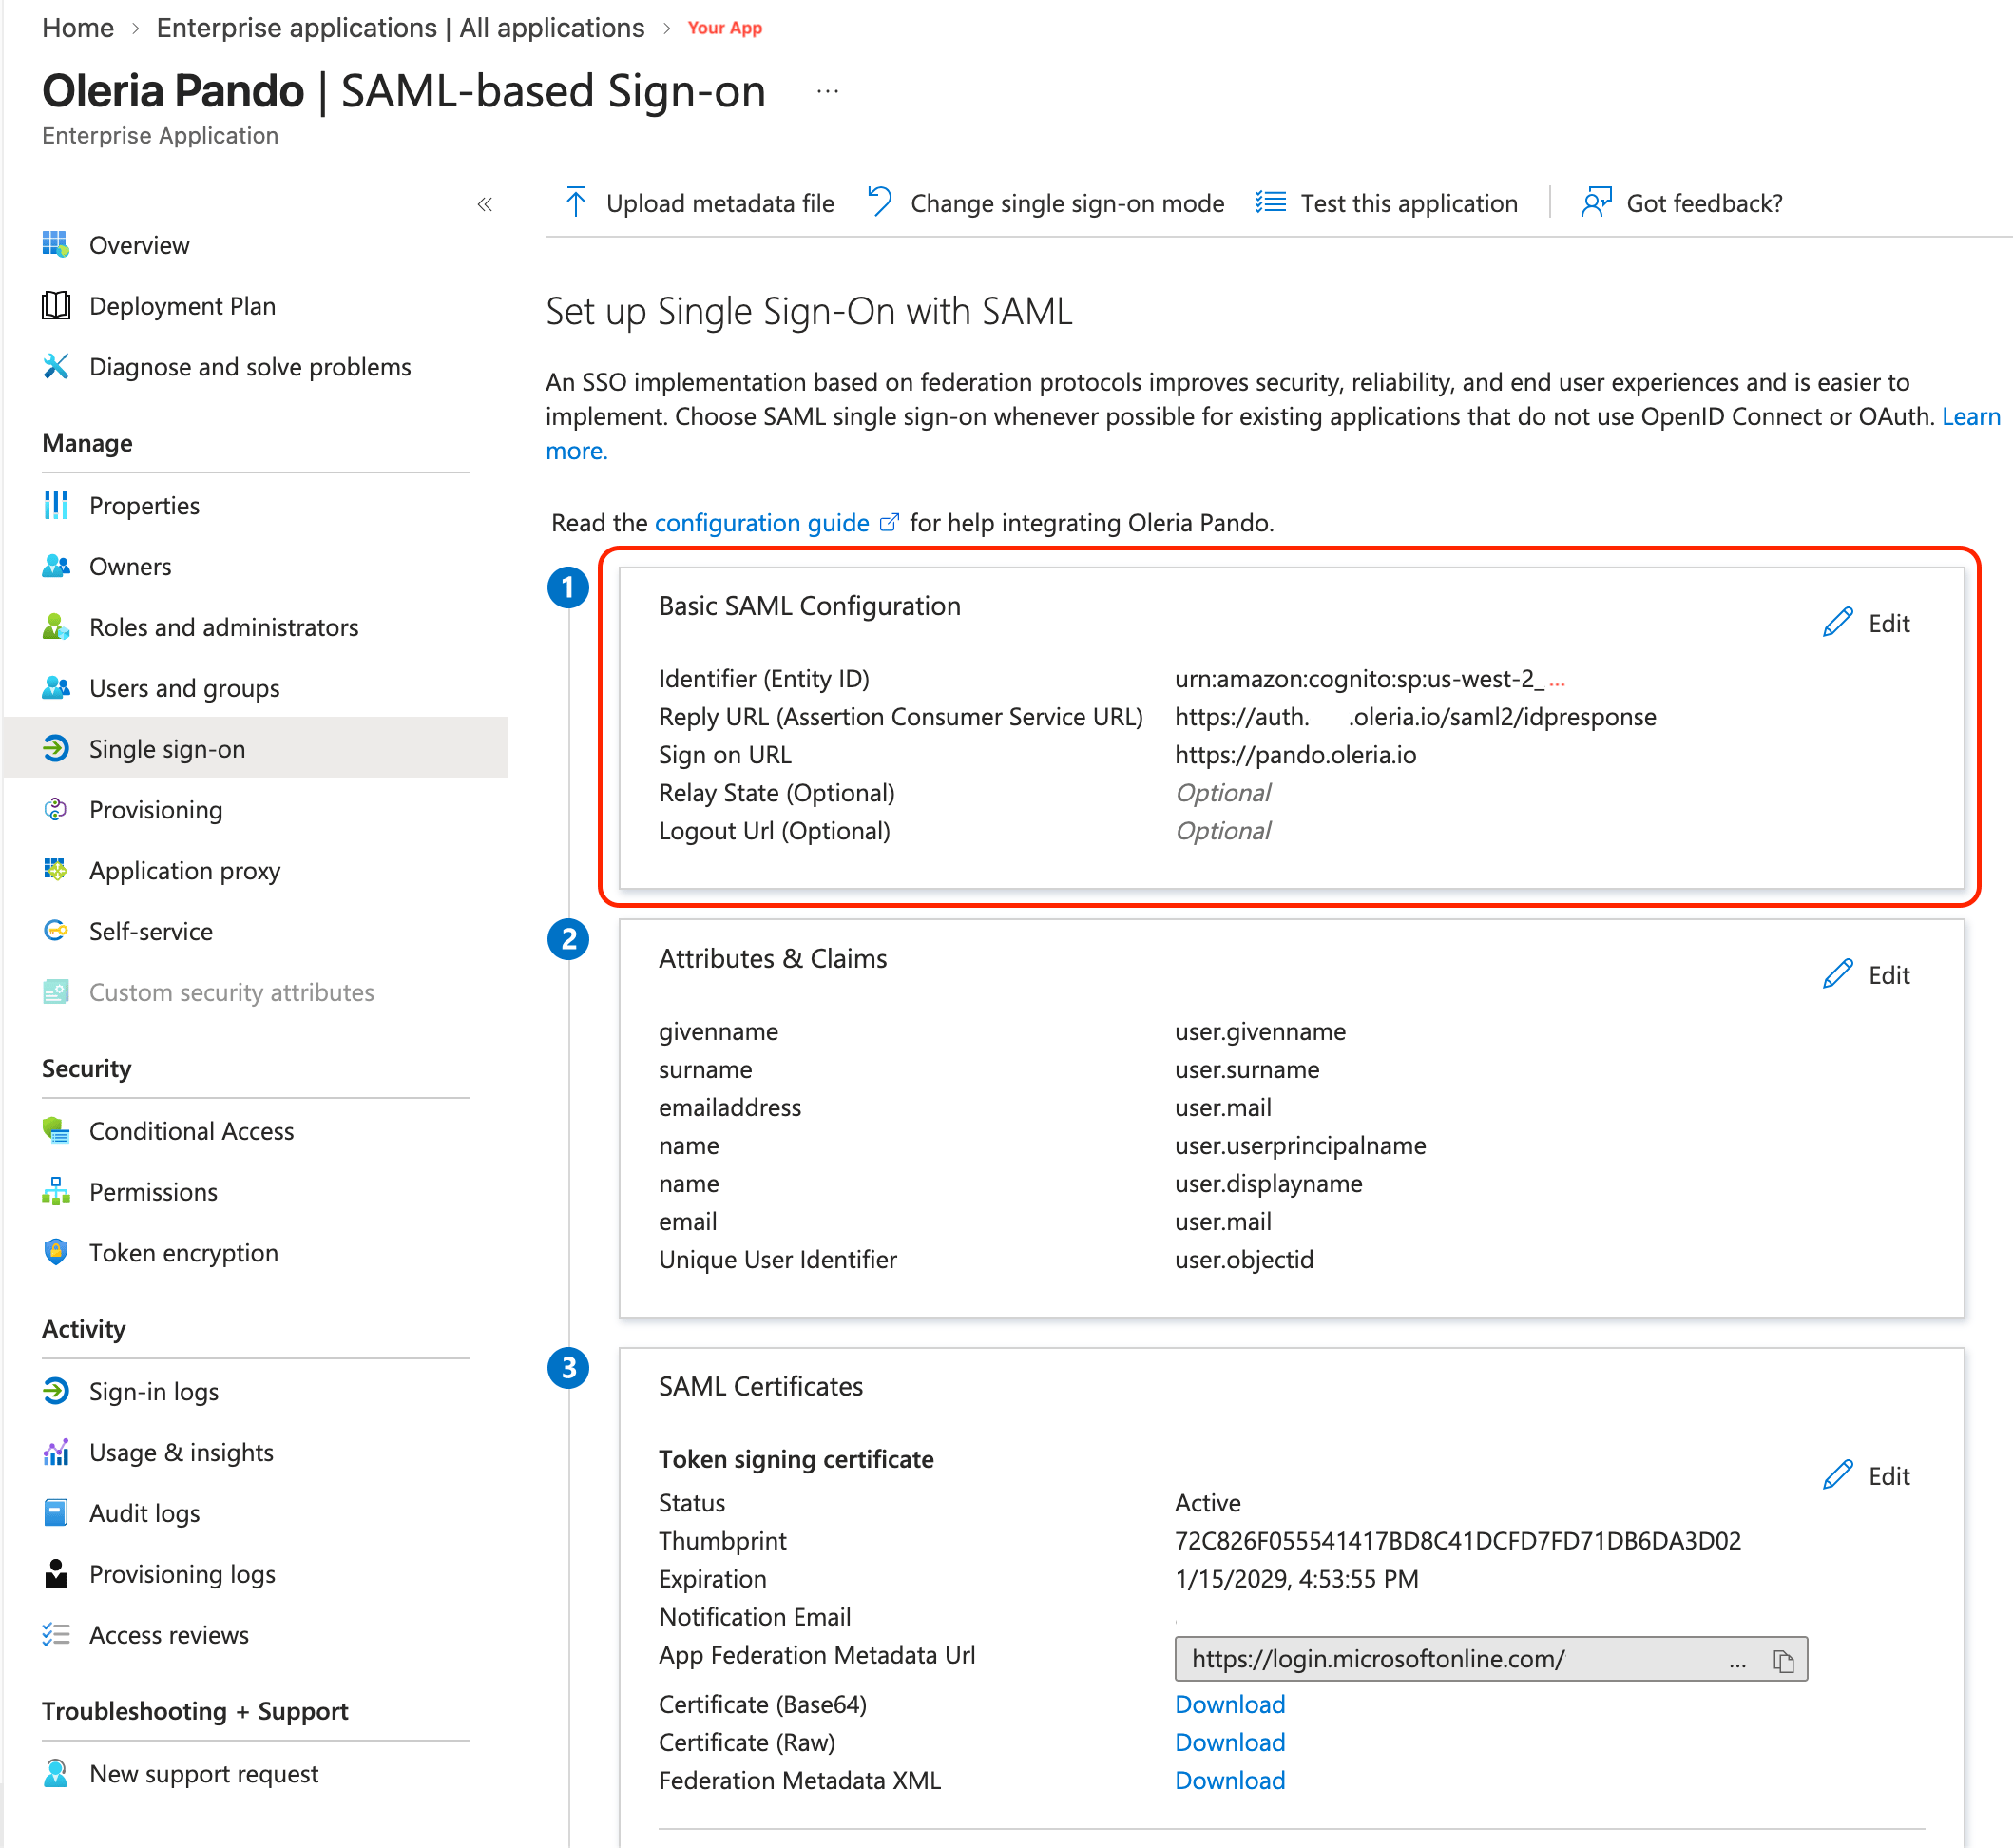
4
Configure the NameID and required claims
In Attributes & Claims: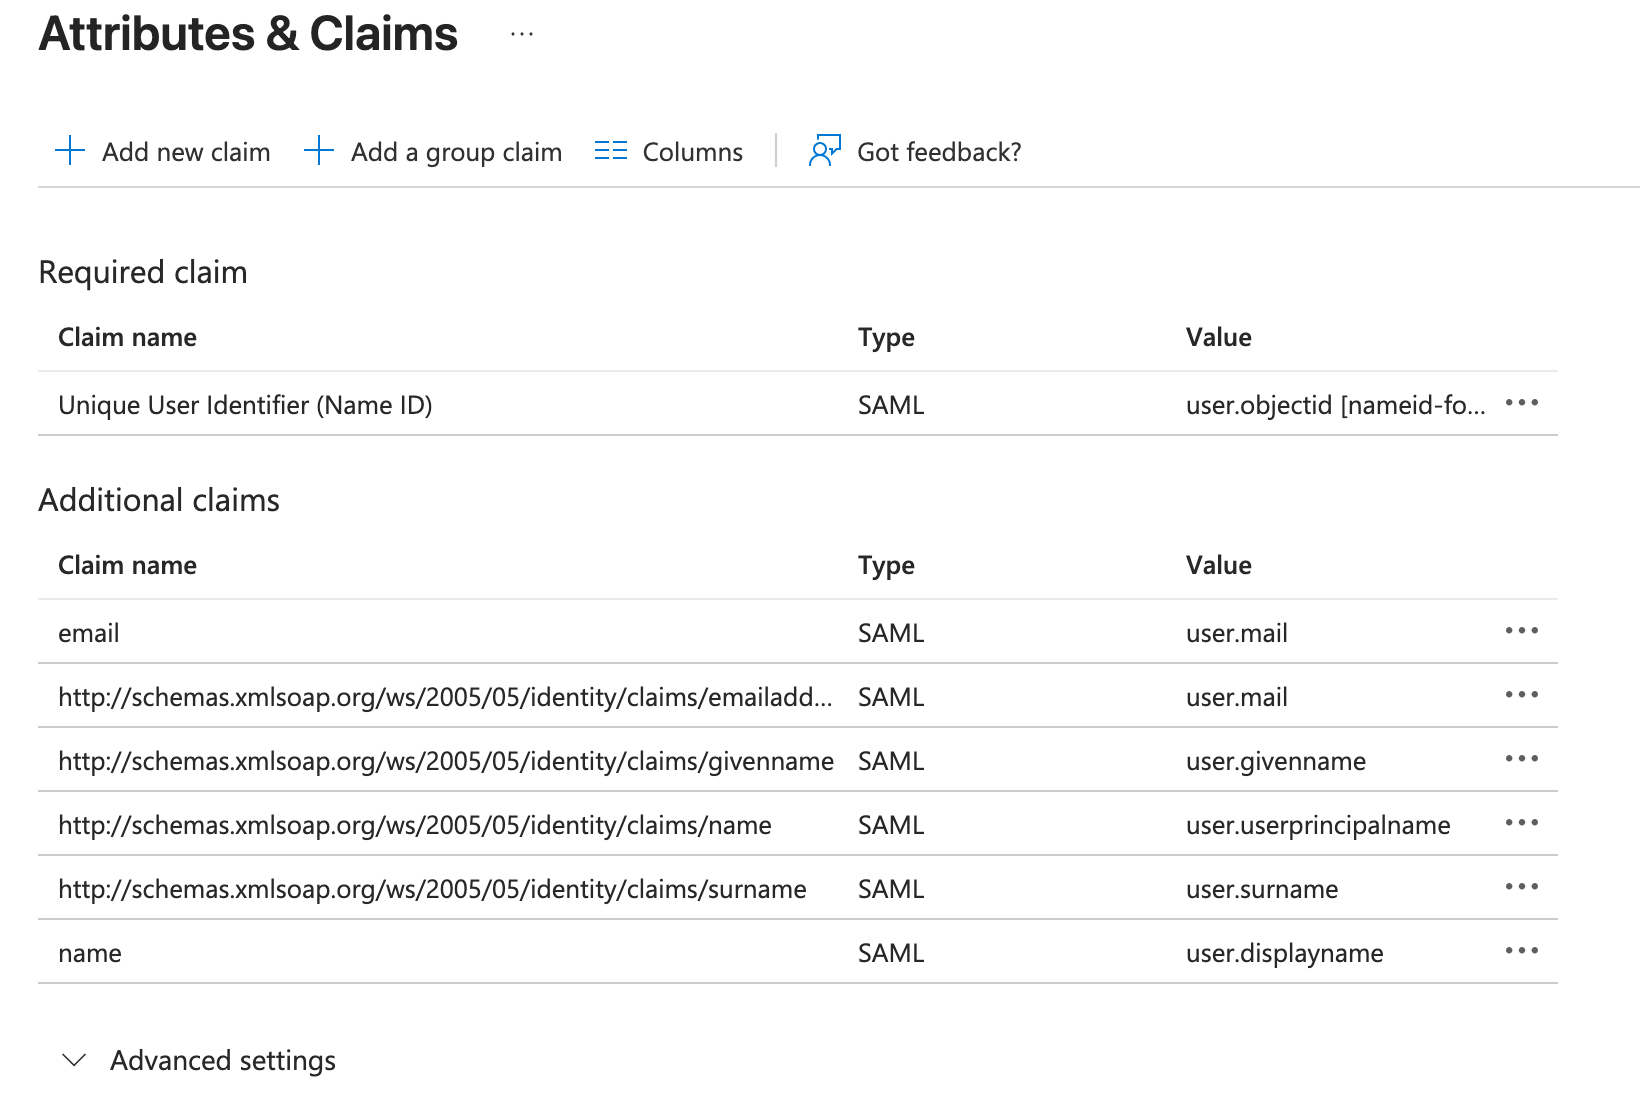
- Edit the Unique User Identifier (Name ID) claim, set Name identifier format to Persistent, and set the Source attribute to
user.objectid(or another stable, opaque identifier) - Oleria’s service provider requires a persistent NameID policy and rejects sign-in otherwise. - Add a new claim named
emailwith source attributeuser.mail, and another namednamewith source attributeuser.displayname. Leave Namespace blank on both - Oleria requires these two exact, short claim names.
5
Assign users and grab the metadata
Assign the users or groups who should be able to sign in through Oleria to the app, then in SAML Certificates, copy the App Federation Metadata Url.
6
Enter the SAML IdP details in Oleria
Back in Oleria, complete the SAML IdP details step: give the provider a Name, paste the Entra metadata URL into Metadata, and decide whether to turn on Sign requests and/or Encrypt SAML responses. Click Add identity provider.
7
If you turned on Sign requests: upload the request signing certificate to Entra
Skip this step if you left Sign requests off. Otherwise, in the Entra app’s SAML Certificates section, click Edit across from Verification certificates, check Require verification certificates, and upload Oleria’s Request signing certificate, downloaded in cer format earlier in this Part.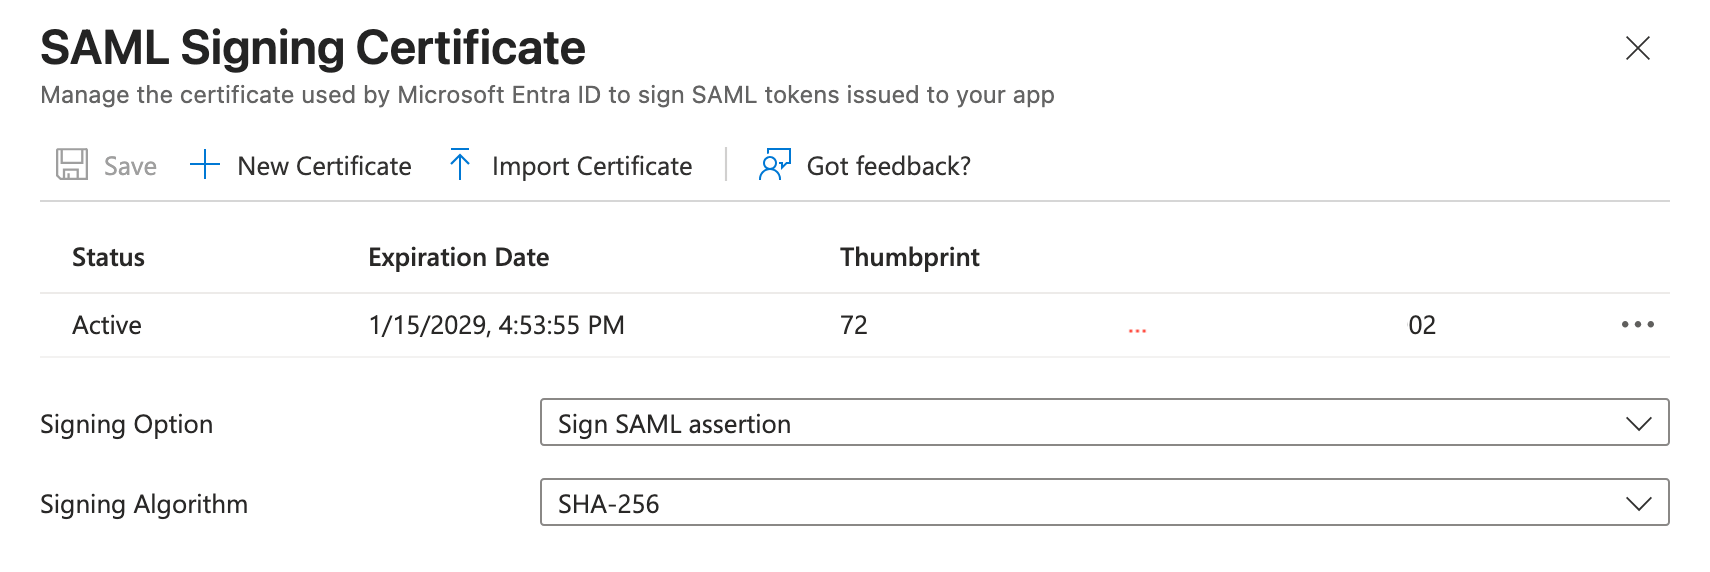
8
If you turned on Encrypt SAML responses: download and upload the response encryption certificate
Skip this step if you turned off Encrypt SAML responses in the Oleria SAML Configuration page.Back in Oleria you’ll see a prompt to download the Response encryption certificate generated specifically for this provider - download it in cer format. In Entra, open the app’s Token encryption page (a separate page from SAML Certificates - requires a Microsoft Entra ID P1 or P2 license), select Import Certificate, upload the certificate, then activate it from the … menu next to the imported certificate.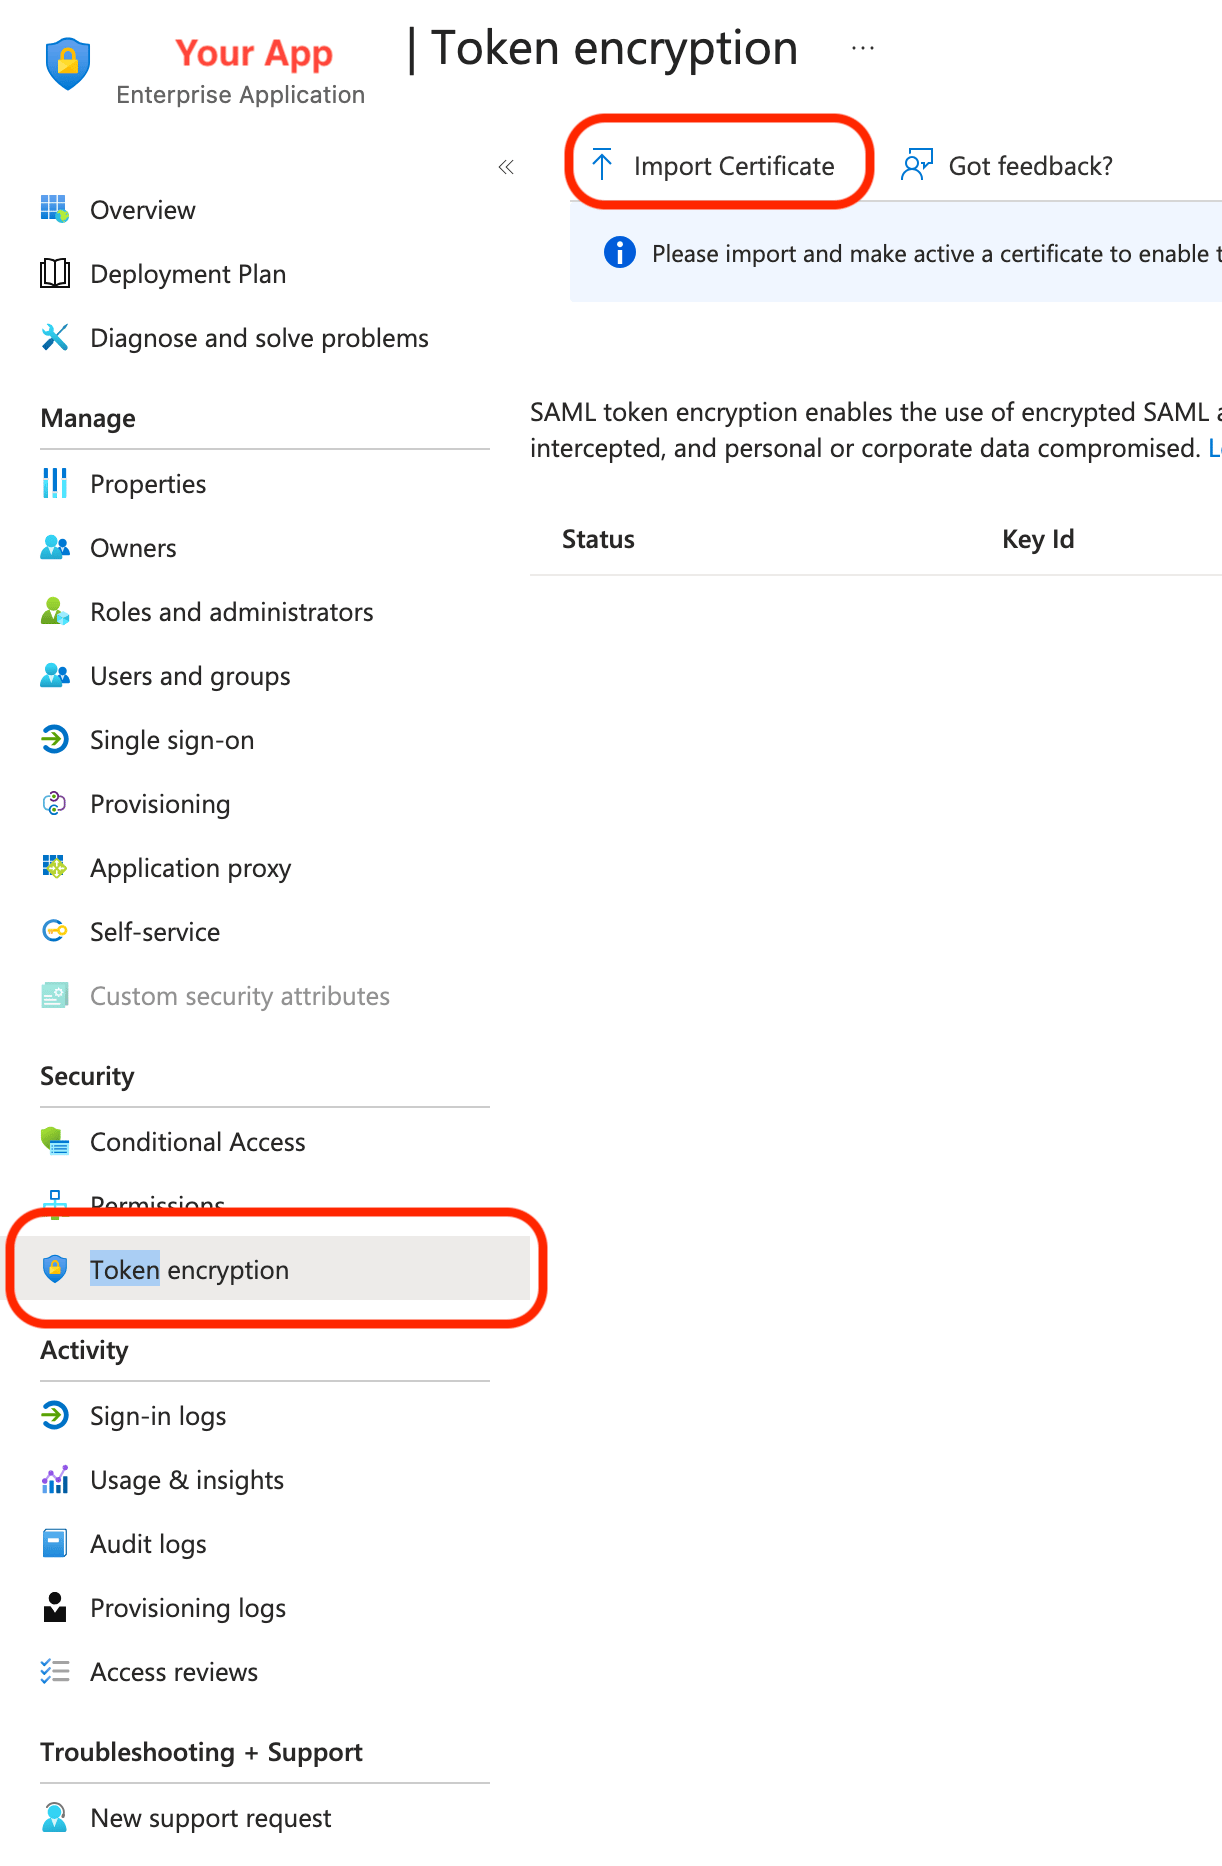
9
Confirm sign-in works
Sign out of Oleria, go to https://www.oleria.com/sign-in, select the new provider, and confirm you land back in Oleria signed in.
Part 2: Set up SCIM
Entra ID P1 or P2 is required for SCIM
1
Get Oleria's SCIM credentials
In Oleria, go to Settings → SCIM Configuration and select the same tab you used in Part 1 (Main Workspace or Governance App). Copy the SCIM Base URL, Client ID, Client Secret, and OAuth Token URL.
2
Open the Provisioning tab
On the same Entra enterprise application from Part 1 (or, if you’re only setting up SCIM without SSO, a new Non-gallery application).
3
Enter the SCIM Connectivity details
In the Connectivity section set the authentication metod to OAuth2 client credentials grant, for Tenant URL paste Oleria’s SCIM Base URL, for OAuth token endpoint paste Oleria’s OAuth Token URL, for Client identifier paste Oleria’s Client ID, and for Client secret paste Oleria’s Client Secret, credentials should be sent by Header, and finally Scope should remain empty. Click Test Connection to confirm Entra can reach Oleria, then click Save.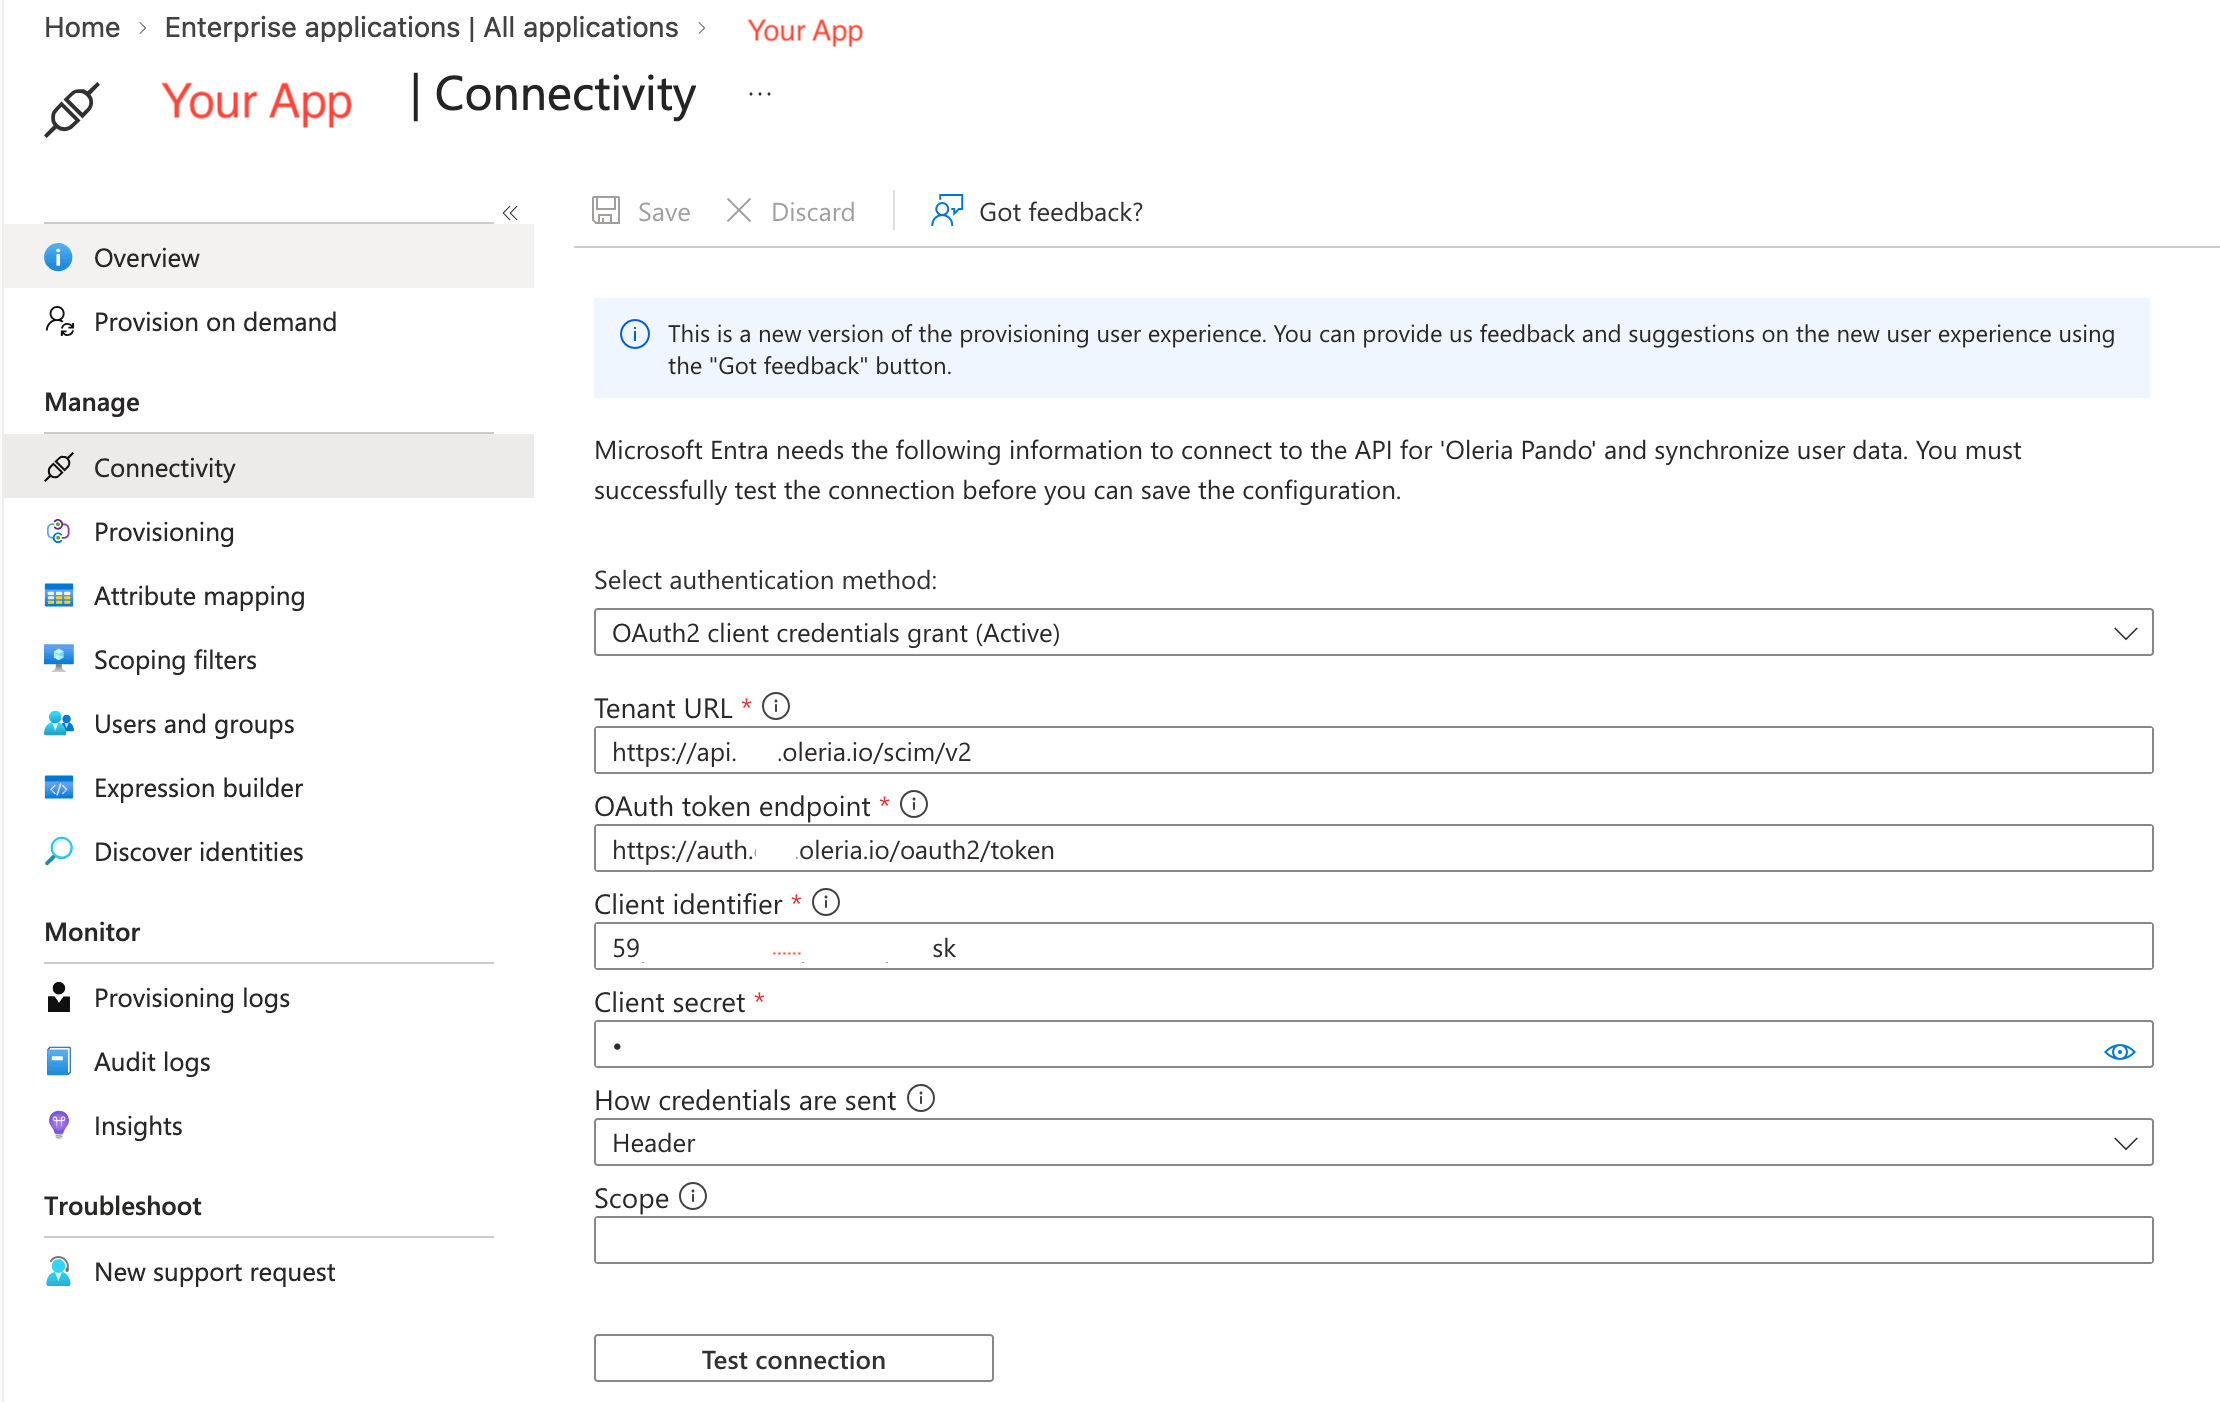
4
Turn on provisioning
In the Provisioning section, set Provisioning Mode to Automatic, and set Provisioning Status to On, then click Save. This enables Entra to call Oleria’s SCIM API and create, update, and deactivate users and groups.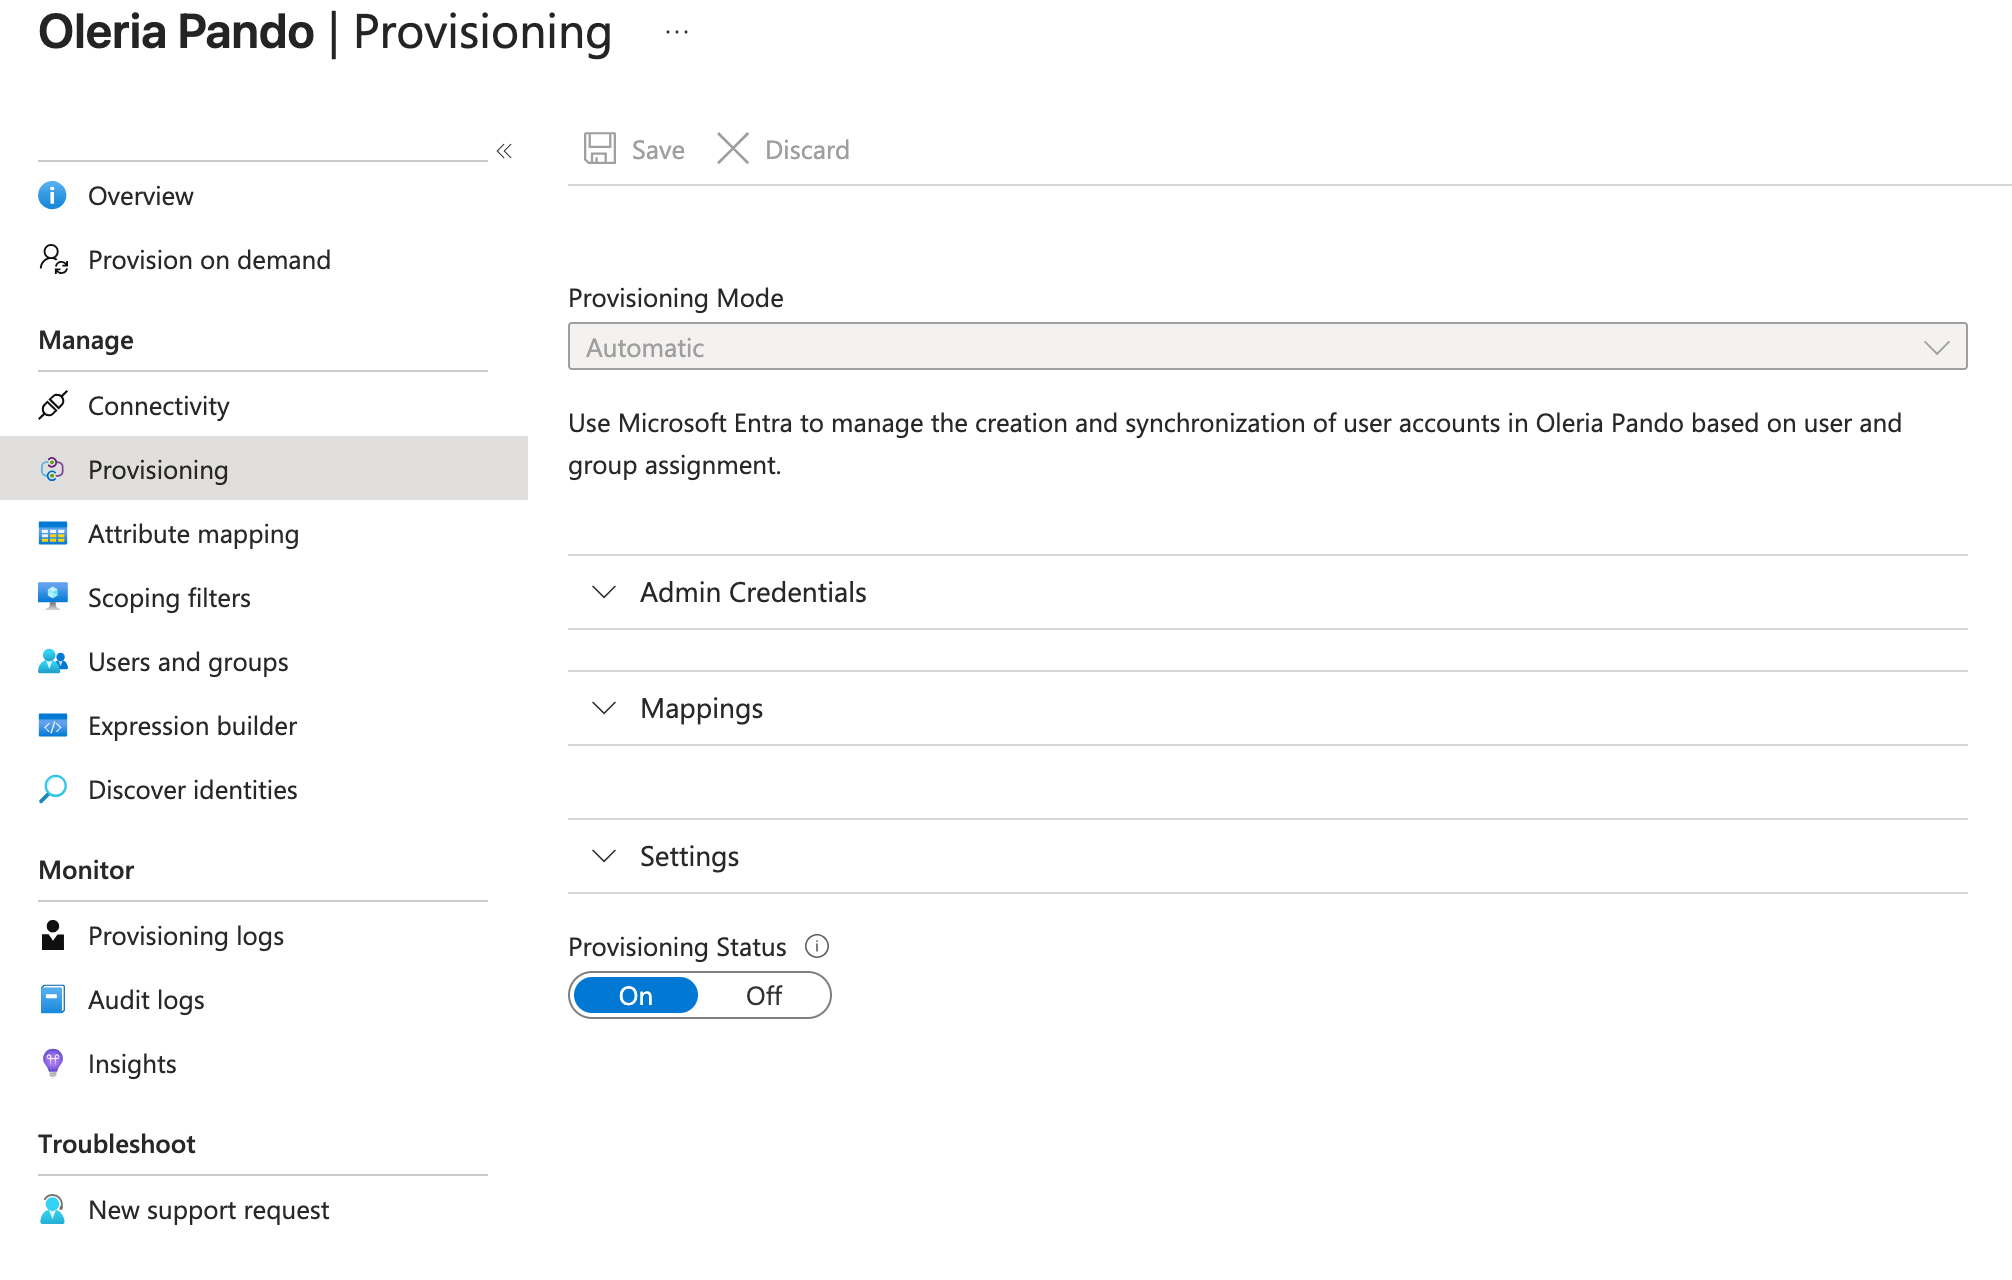
5
Review the attribute mappings
Entra proposes default attribute mappings for Provision Microsoft Entra ID Users.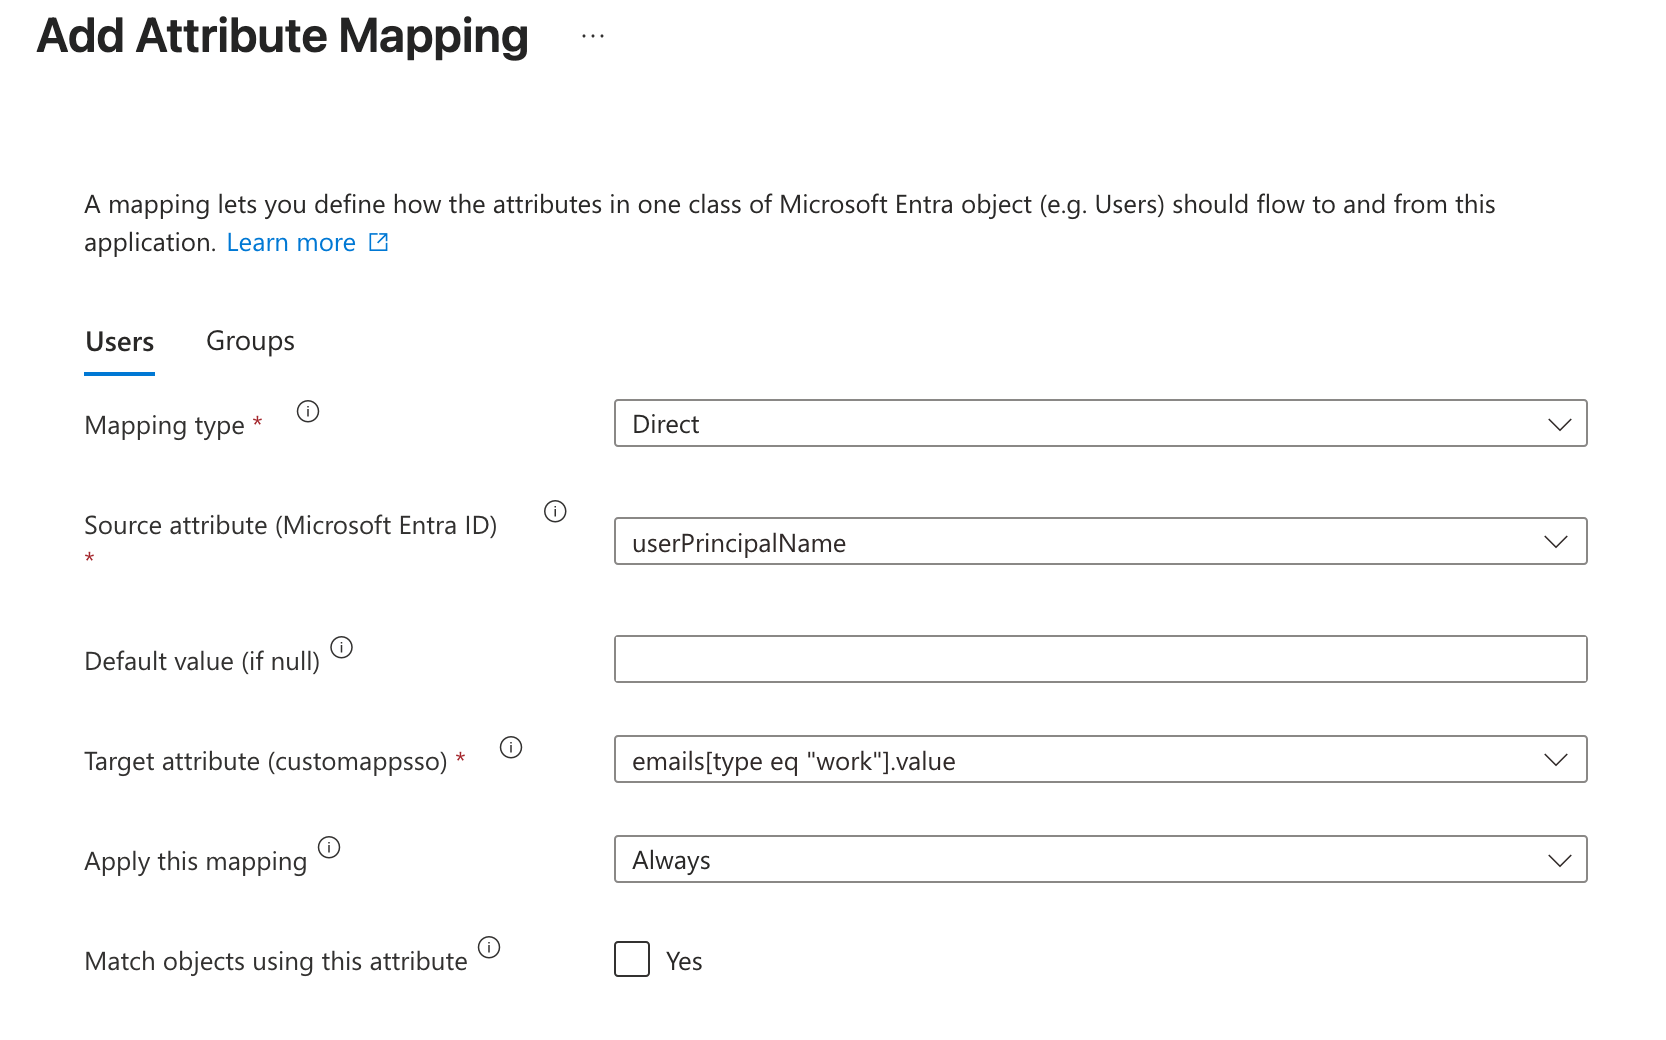
- Confirm
userPrincipalName(or another attribute holding the user’s email) maps touserName. - Confirm that either the name parts or
name.formattedor both are mapped. This should exist by default. - Confirm that
userPrincipalName(or another attribute holding the user’s email) maps toemails[type eq "work"].value, this mapping defaults tomailbut that is not commonly used anduserPrincipalNameis more reliable.
Main Workspace only: Oleria grants roles through group membership, not directly on the user (see How Oleria maps roles and groups). Leave Provision Microsoft Entra ID Groups enabled so group membership syncs along with users.Governance App: there is no group-to-role mapping to configure - every provisioned user is assigned the single
reviewer role automatically. You can turn group provisioning off and provision users only.6
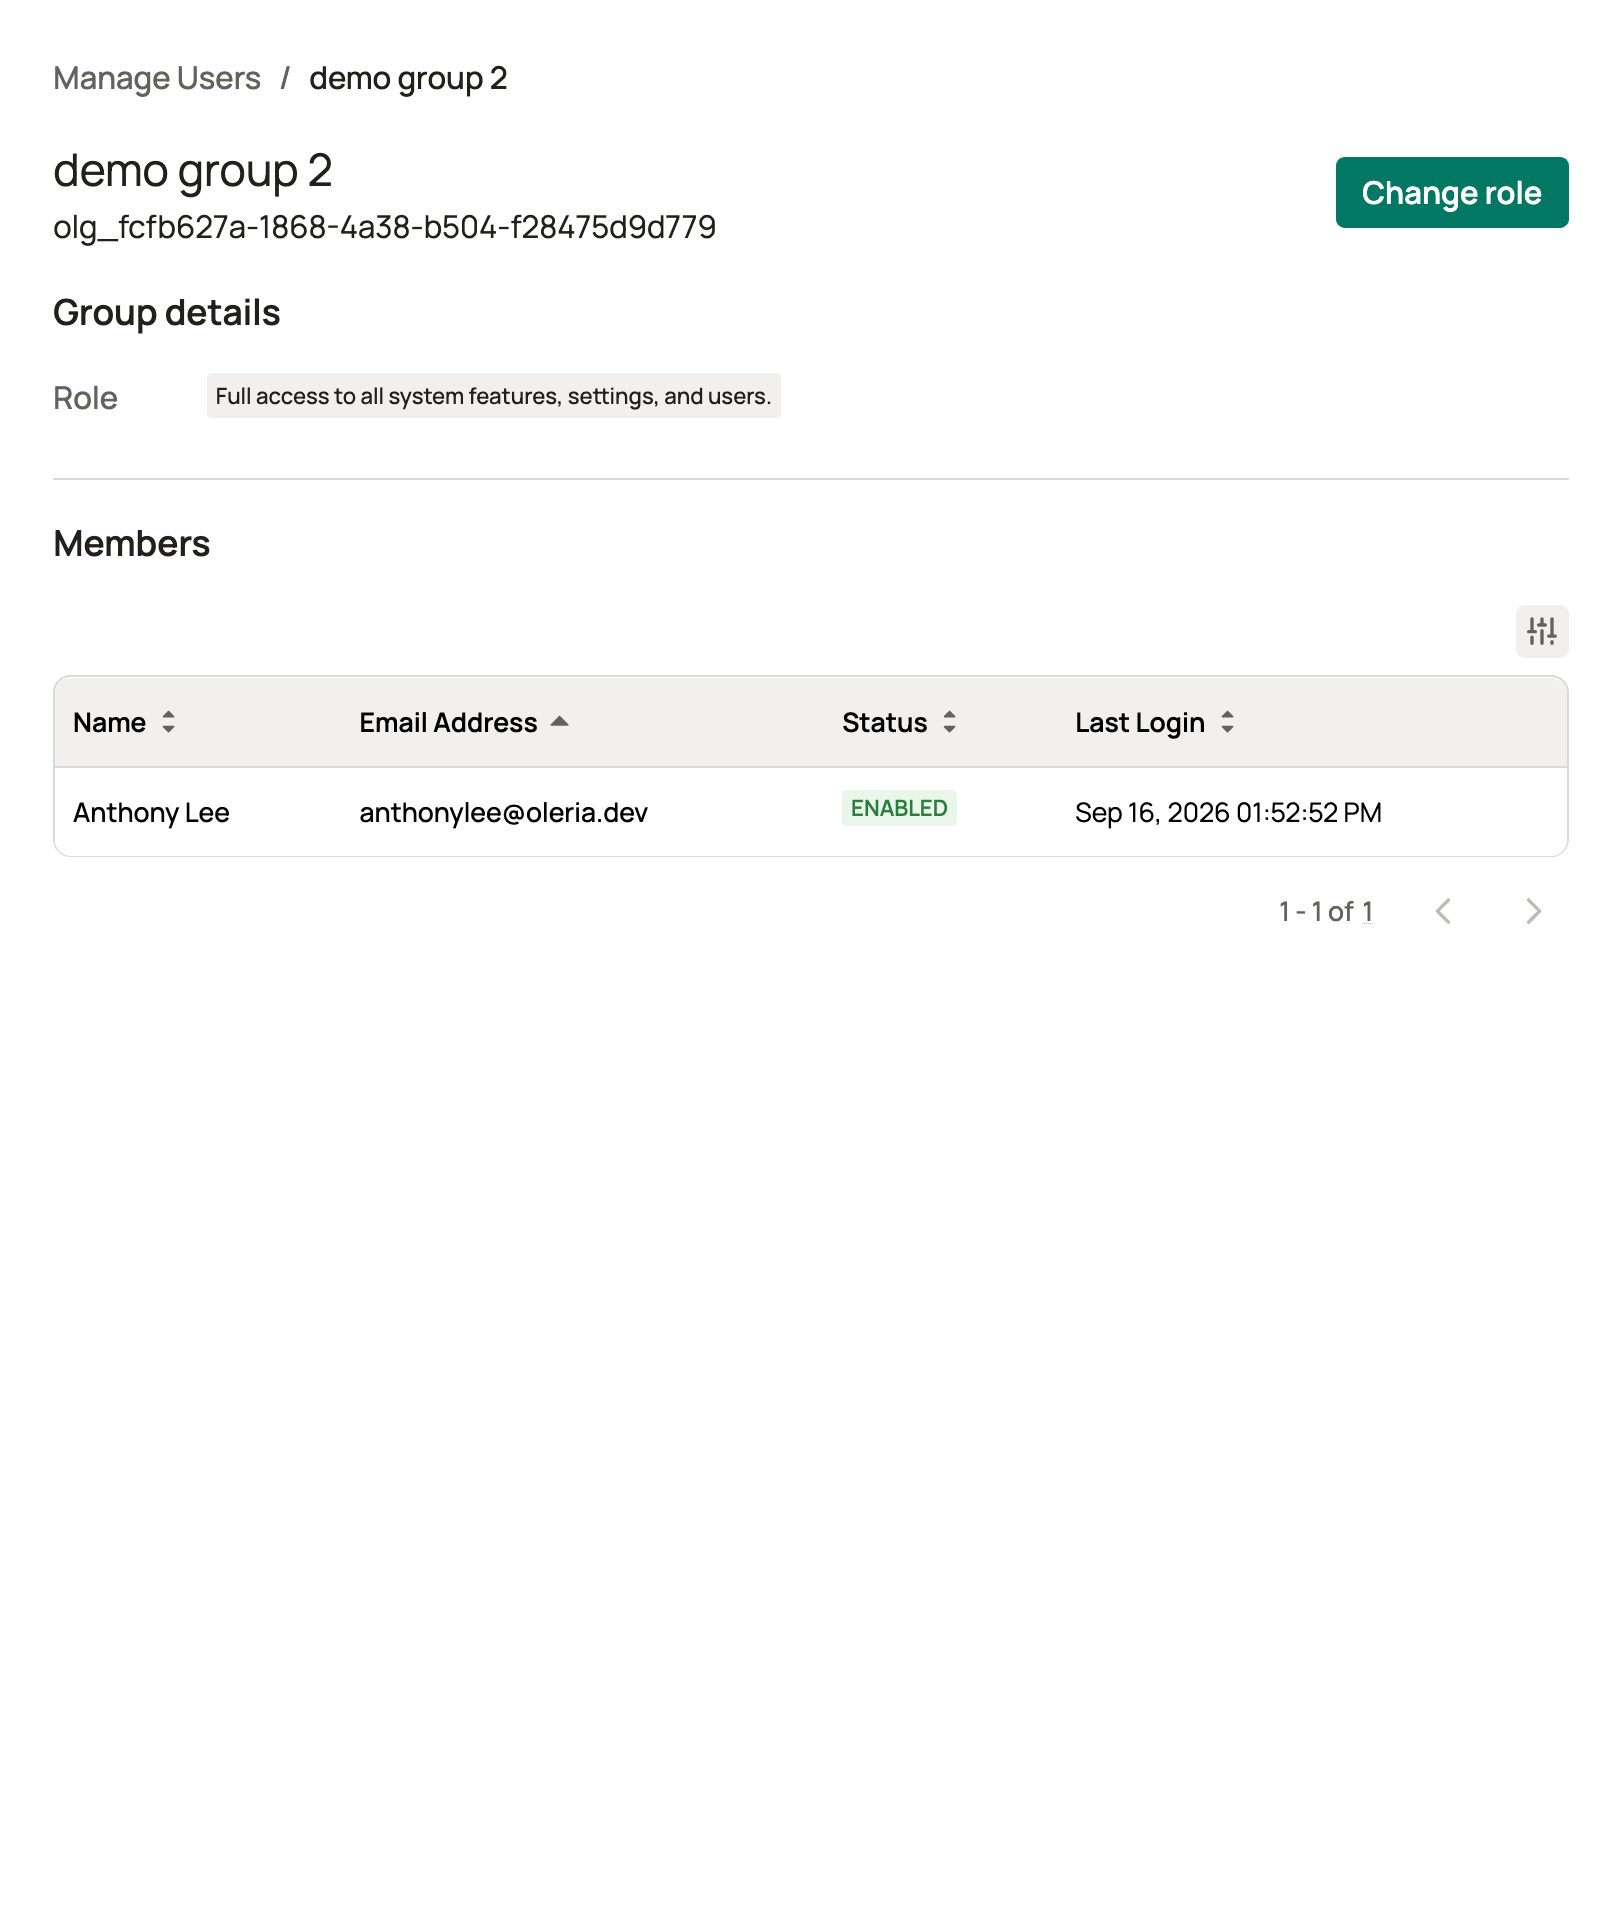
Main Workspace only: assign each group a role in Oleria
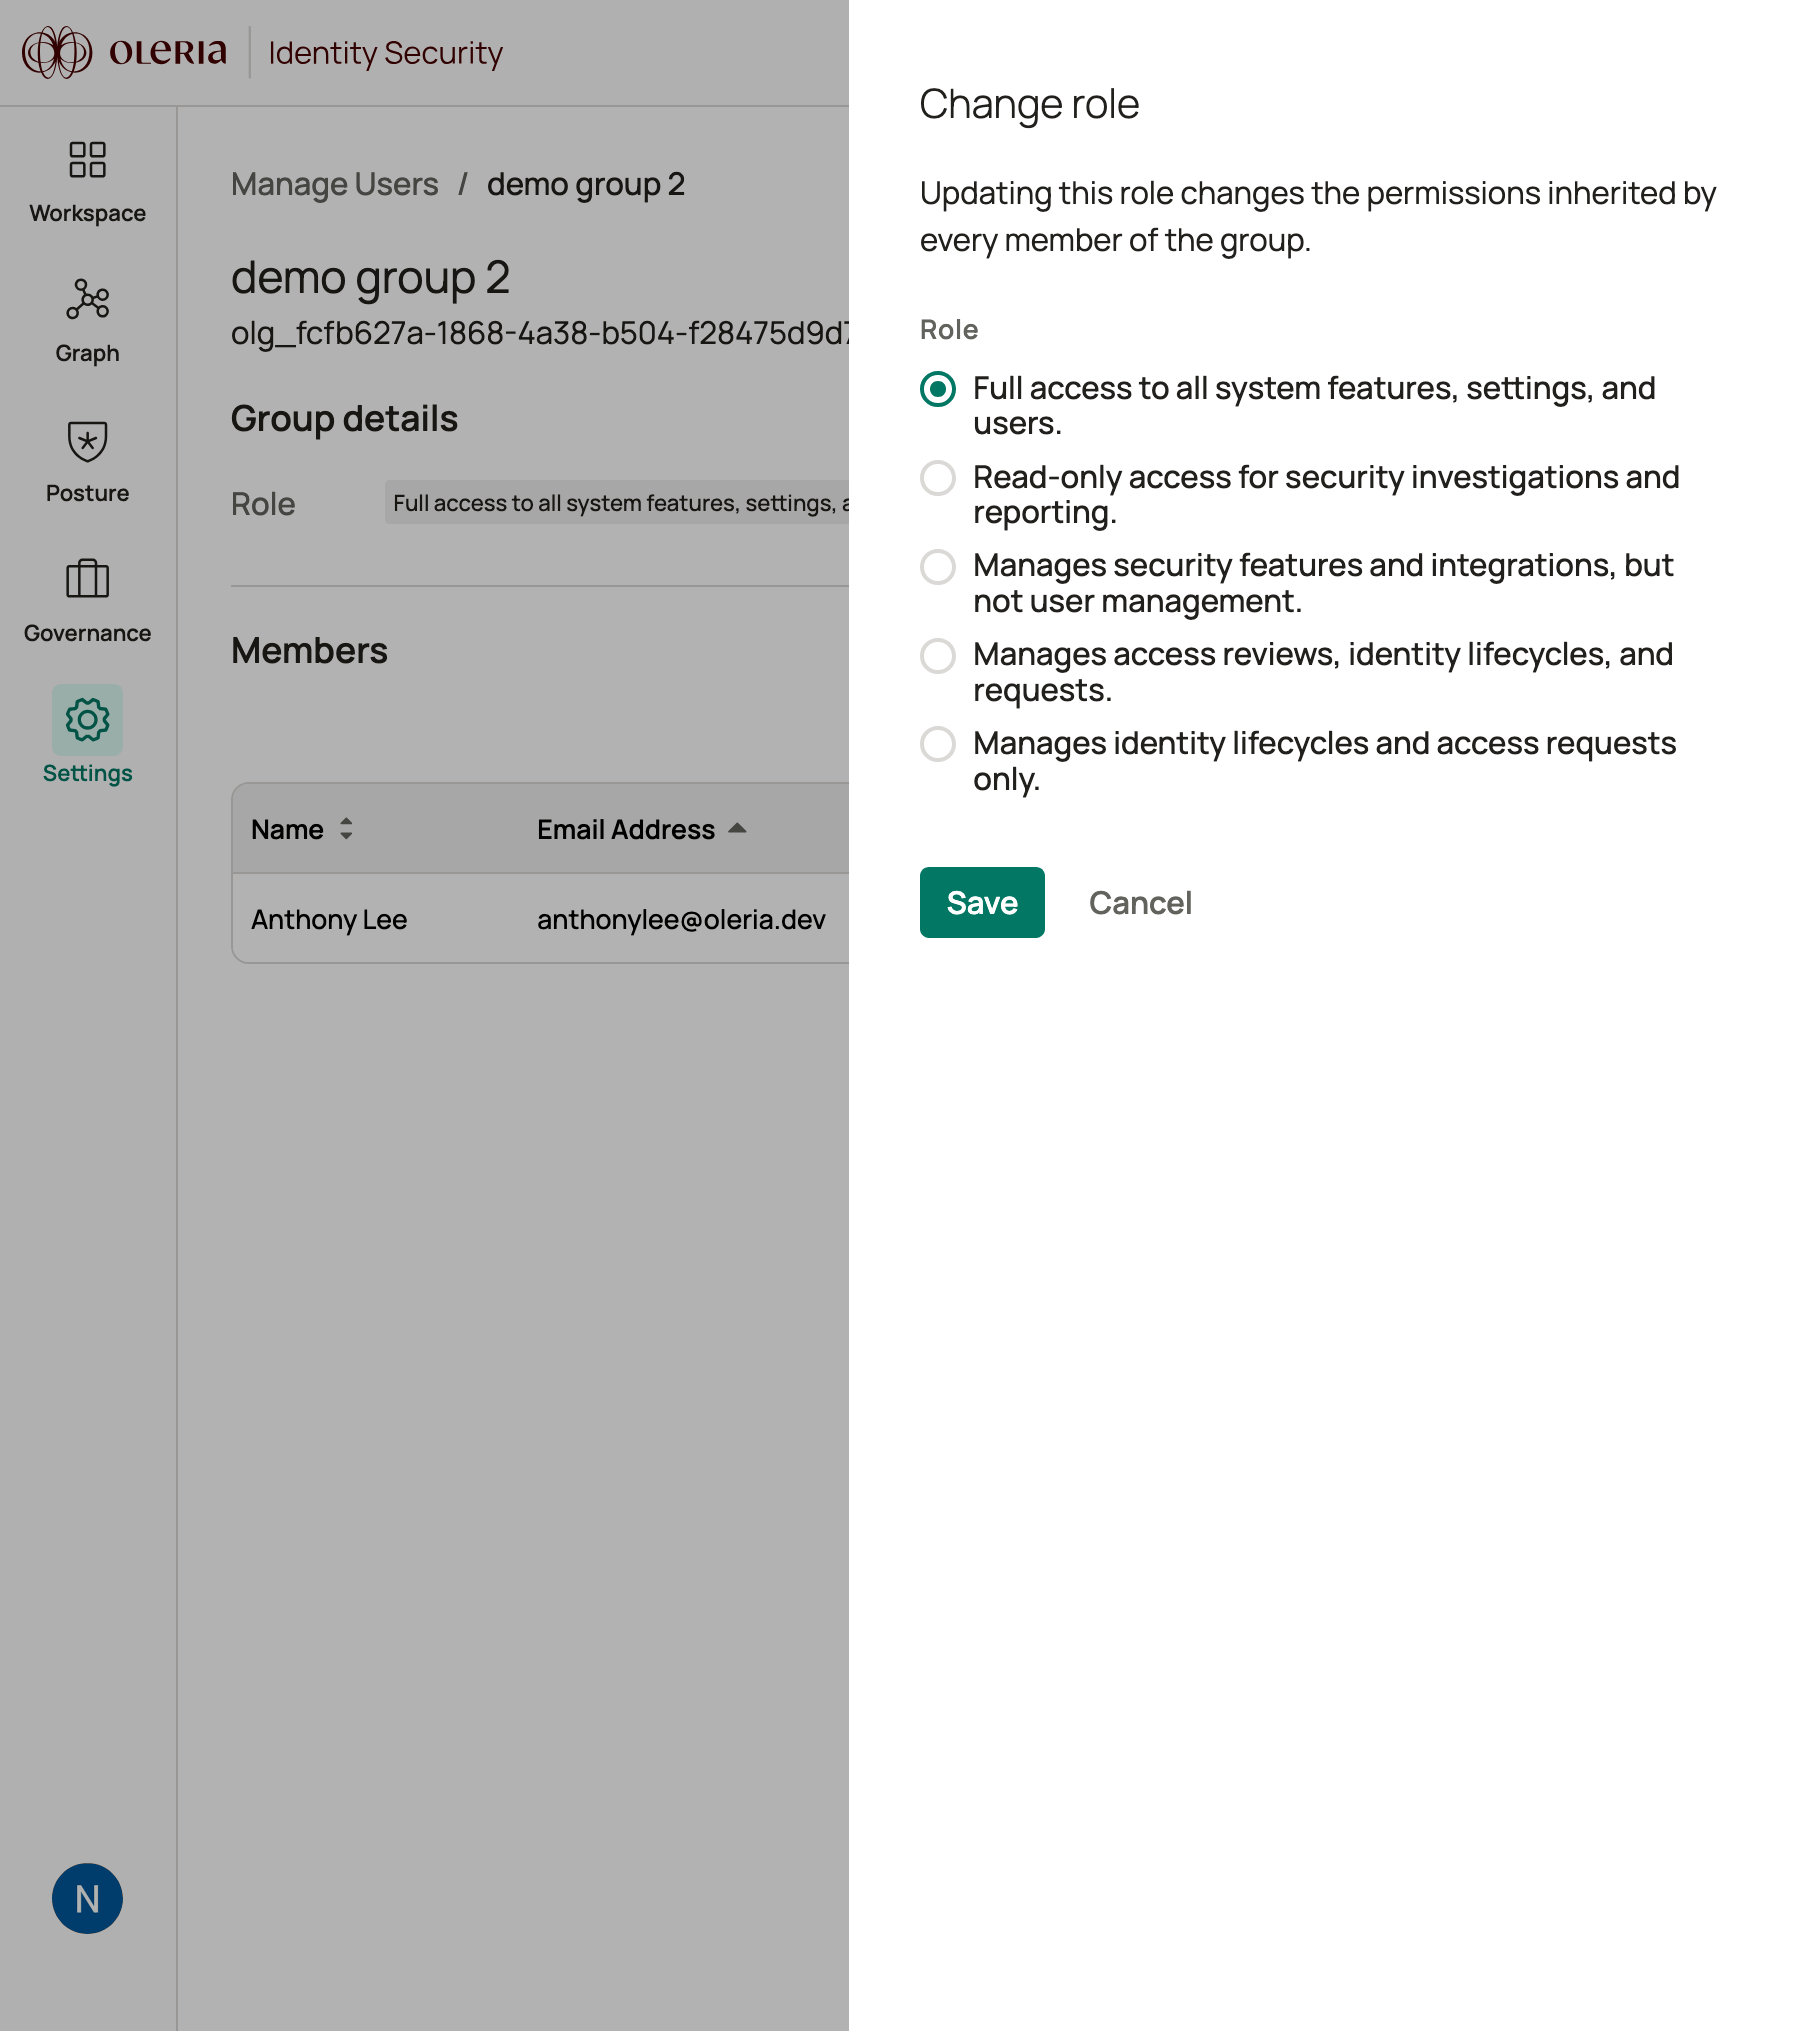
In Oleria, under Settings open Manage Users, select the Groups tab, and for each group you push, select it, click Change role, choose the role it should map to, and click Save. Every current and future member of the group inherits that role. See Assign a role to a group for the full walkthrough.Oleria’s Manage Users page: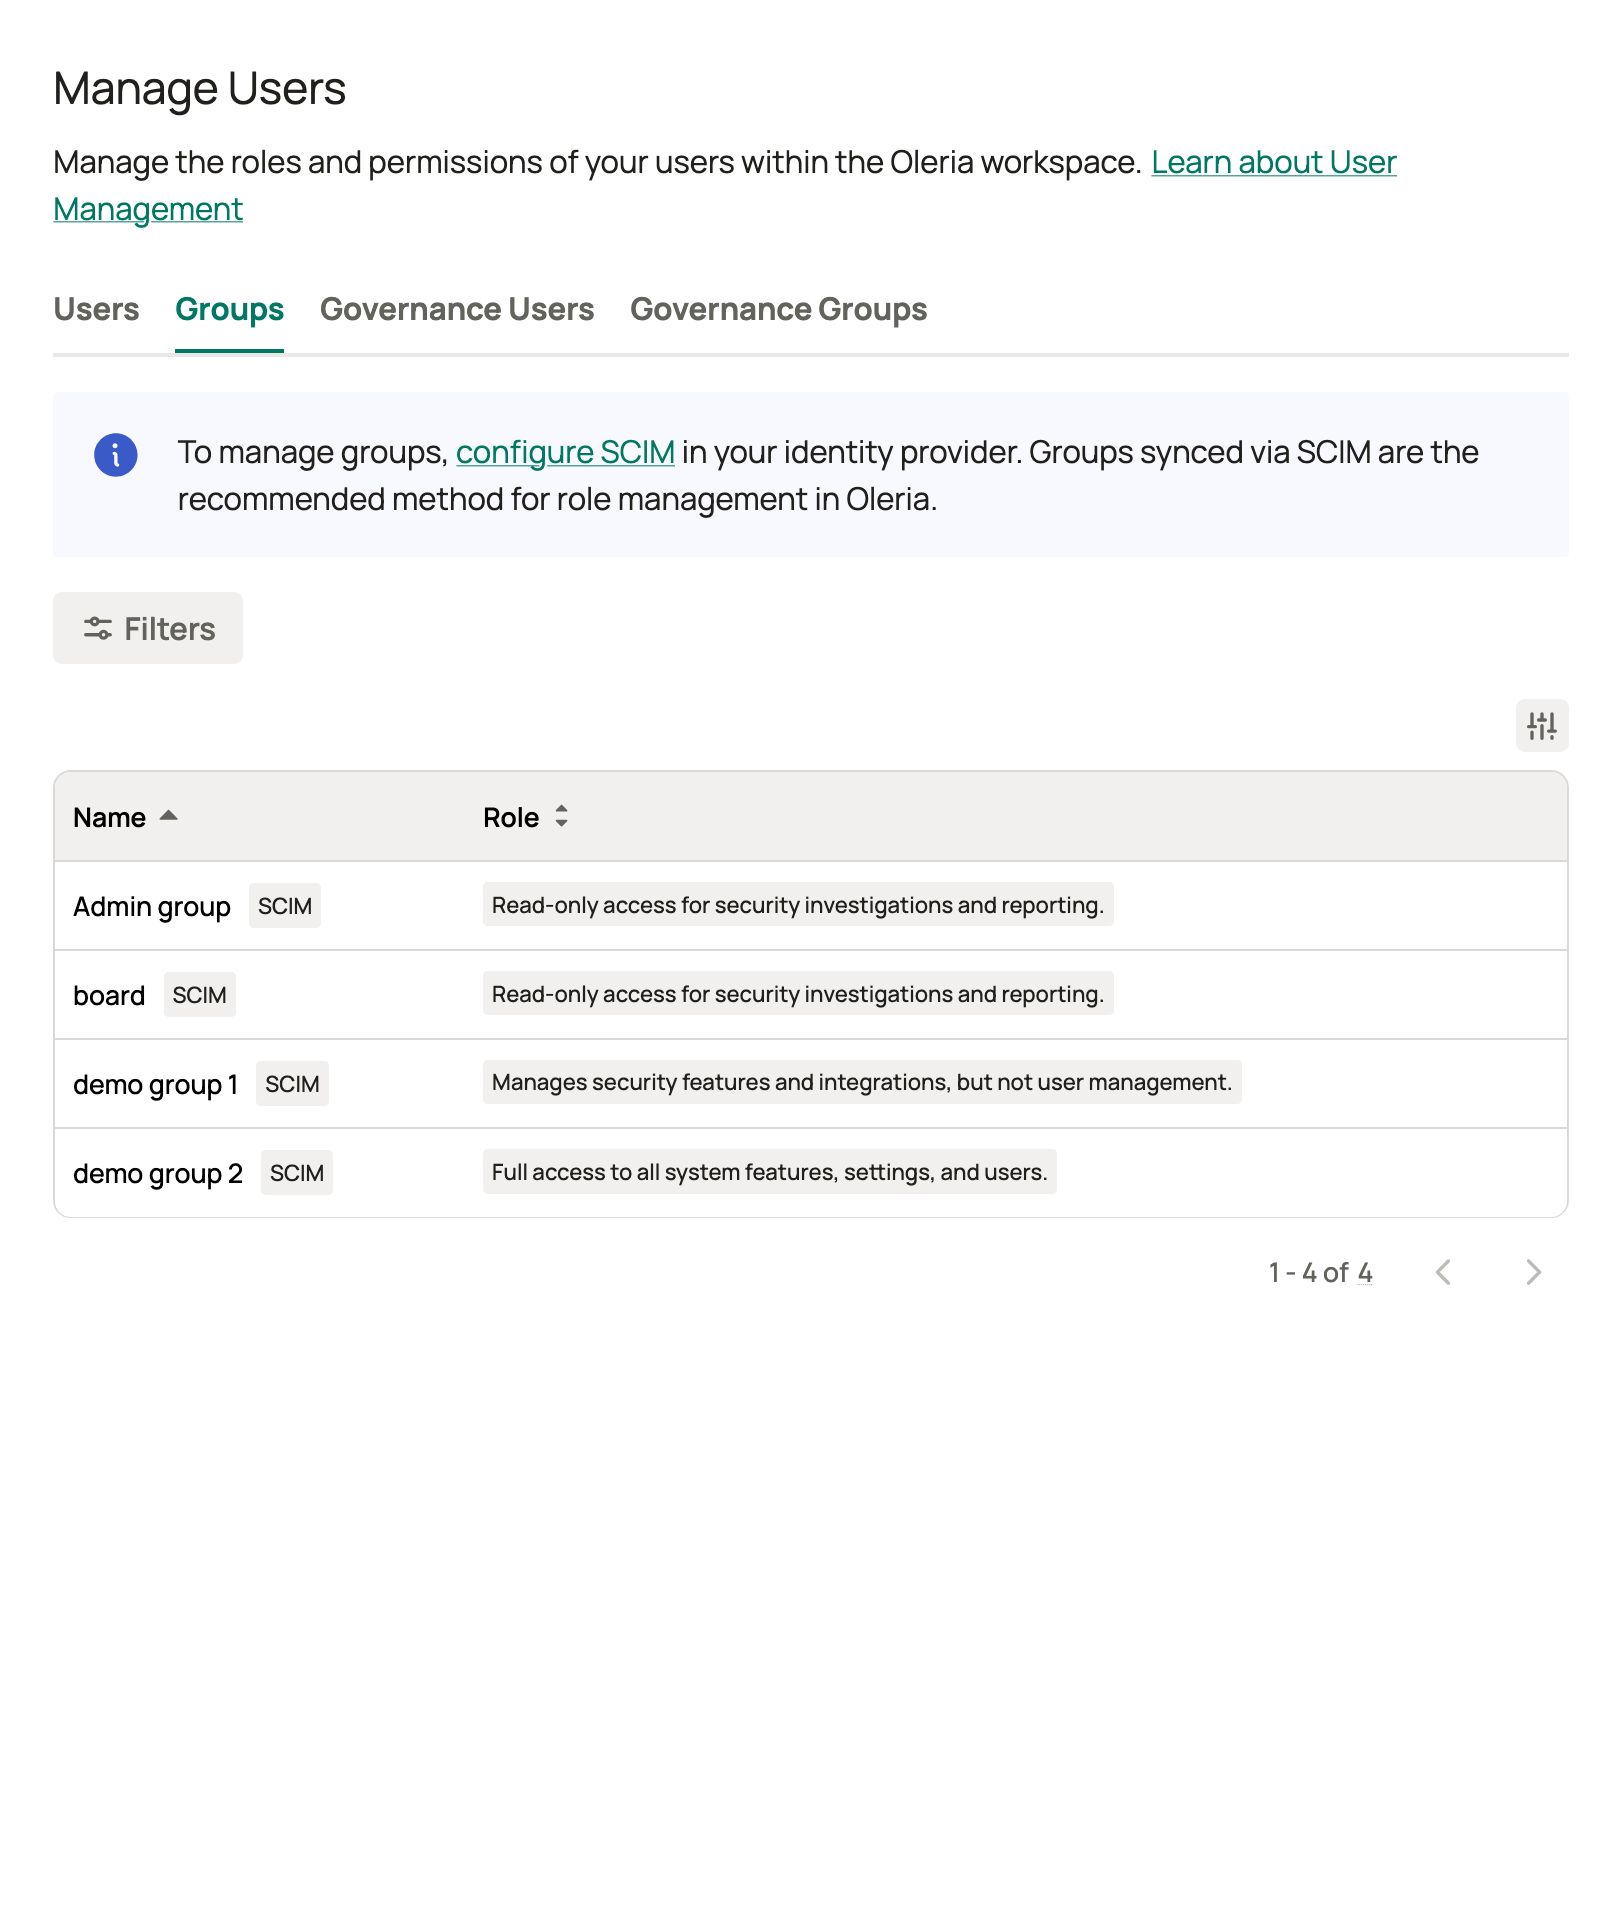
7
Scope and start provisioning
Under Users and groups, assign the users or groups that should get Oleria accounts. On the Provisioning tab, set Scope to Sync only assigned users and groups (recommended over syncing the whole directory), then click Start provisioning.
8
Verify
Watch the Provisioning tab’s sync status - the first cycle can take anywhere from about 20 minutes to a few hours. In Oleria, confirm the new users appear (Main Workspace: in Manage Users with the expected role; Governance App: in the governance reviewer list). Unassign a test user in Entra and confirm they lose access in Oleria on the next cycle.
Alternative for the Governance App: if you don’t need directory-driven deprovisioning and don’t want to build the Entra provisioning connector above, you can skip this Part entirely and use Oleria’s built-in automatic user provisioning instead - it only requires SSO (Part 1) to already be working. Follow Automatically provision reviewers to enable it and set allowed email domains. Remember this is not SCIM: it only creates accounts on sign-in and never deactivates them, so it’s not a substitute for SCIM if you need automatic offboarding.
Alternatives without Entra ID P1
If your tenant is on Entra ID Free and adding P1 isn’t an option, these are the working paths. They’re the same options as the Okta equivalent, since the constraint is on the identity provider side rather than Oleria’s.
A common split is automatic user provisioning for the Governance App reviewer population plus hand-managed Main Workspace admins - that combination needs only SSO, and no P1.
Set up the second workspace
If you need both workspaces connected to Entra, don’t repeat Part 1 with a new enterprise application - see Entra’s one-app-per-Entity-ID rule above. Instead:- SSO: in Oleria, go to the SSO Configuration page and select the tab for the workspace you have not yet set up. Add an identity provider using the same Entra app’s App Federation Metadata Url from Part 1.
- SCIM: Entra allows only one provisioning job per enterprise application, so you can’t add a second Provisioning configuration to the same app you used for SSO. Create a second Non-gallery application instead, used for provisioning only - leave its Single sign-on section unconfigured entirely. Entra’s Entity ID uniqueness rule only applies to apps with SAML SSO configured, so a provisioning-only app with no SAML section touched never collides with it. Point this second app’s Provisioning details at the other workspace’s SCIM Base URL, OAuth Token URL, Client ID, and Client Secret, following Part 2 again on the new app.
Troubleshooting
- The Provisioning section is unavailable, won’t accept Automatic mode, or groups never sync while users do: see Entra ID P1 or P2 is required for SCIM, and Alternatives without Entra ID P1 if you can’t upgrade
- Adding or editing the identity provider in Oleria: Troubleshoot identity provider errors
- Sign-in failures after the provider is saved: Troubleshoot sign-in failures
- “Please enter an identifier which is unique within your organization” when creating a second Entra app: see Entra’s one-app-per-Entity-ID rule - use one shared app instead of two.
- SCIM request/response errors: the SCIM user provisioning and Governance App SCIM provisioning reference pages cover the request and response shape for every endpoint.