Only Oleria Administrators can change how an application is credentialed. View role permissions.
Why this matters
Using your own OAuth app moves several security controls from Oleria to you. You hold the revocation switch. You can block or delete the connected app in Salesforce at any time, and every gateway connection made through it stops. You don’t have to raise a ticket, and you don’t have to wait for Oleria to act. The scope ceiling is yours. The gateway can never receive more than the OAuth scopes your connected app permits. Narrowing the app narrows every agent’s reach, immediately and unilaterally. Your provider’s own controls apply. A connected app you own can be restricted to pre-authorized users, locked to your corporate IP ranges, and given your own refresh-token lifetime and session policy. Those controls sit in Salesforce, enforced by Salesforce, whether or not Oleria’s policy agrees. The audit trail is on your side too. Salesforce attributes OAuth usage and API calls to the connected app that made them. With your own app, your security team can see gateway activity in your own logs rather than relying solely on Oleria’s. Your access doesn’t share fate with anyone else’s. Oleria’s OAuth app is one client used across customers. With your own client ID and secret, a revocation, rotation, or provider-side rate limit affecting Oleria’s app doesn’t affect you. The client secret you provide is encrypted with your tenant’s own key and never shown back to you after saving. Oleria uses it only to complete the OAuth flow and to refresh tokens.Before you start
You need administrator access in Salesforce to create a connected app, and the Oleria Administrator role to configure it in the gateway. Have the gateway’s callback URL to hand. Salesforce rejects an authorization request whose redirect URI doesn’t match the connected app exactly:Create the connected app in Salesforce
1
Start a new connected app
In Salesforce Setup, go to App Manager and select New Connected App. Give it a name your administrators will recognize, such as
Oleria AI Agent Gateway, and supply a contact email.2
Enable OAuth and set the callback URL
Select Enable OAuth Settings, then paste the callback URL above into Callback URL.Leave Require Secret for Web Server Flow enabled. The gateway is a confidential client and always sends the secret.
3
Select the OAuth scopes
Add the scopes the gateway needs:
Add nothing else. These are exactly the scopes the gateway requests - see Application permissions - and a broader connected app grants access that nothing will use.
4
Save and collect the credentials
Save the connected app. Salesforce can take several minutes to make a new app available.Then open Manage Consumer Details and copy the Consumer Key and Consumer Secret. The secret is shown once.
5
Restrict who may use it
This step is optional, and it is the reason most organizations bring their own app.Under Manage -> Edit Policies, set Permitted Users to Admin approved users are pre-authorized, then grant the app only to the profiles or permission sets that should be able to use agents. Set IP Relaxation and the refresh-token policy to match your standards.With Admin approved users are pre-authorized, anyone not on the list cannot connect Salesforce through the gateway at all, regardless of Oleria’s configuration.
Add it to Oleria
1
Open the application's policy panel
In the admin portal, go to Governance -> Oleria AI Agent Gateway, and on the OAuth Access tab select the Salesforce row.
2
Turn on bring your own credentials
In Registry, turn on Bring your own credentials. Three fields appear.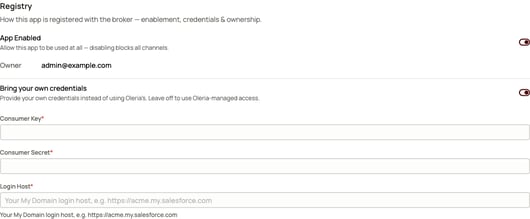
Set Login Host to the host people actually sign in to. A sandbox or a custom My Domain will not authenticate against the default Salesforce login host.
3
Save
Select Save. All three fields are required - the gateway won’t switch to your app until each is supplied.To go back to Oleria’s OAuth app, turn the toggle off and save again.